Presents
Magnus Mårtensson
Microsoft Regional Director, Azure MVP, CEO Loftysoft
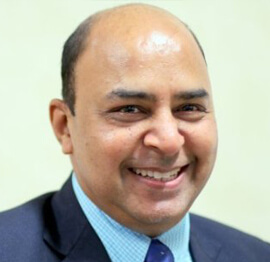
Avirag Jain
Director & CTO R Systems
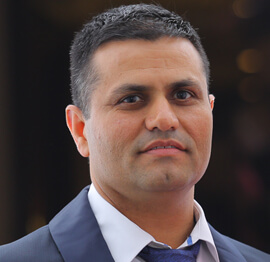
Mahesh Chand
Founder C# Corner, CEO Mindcracker
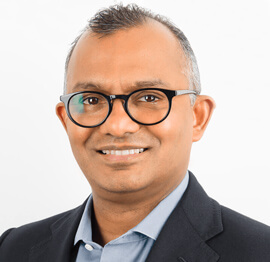
Chris Gali
CEO & Co-Founder Graphite
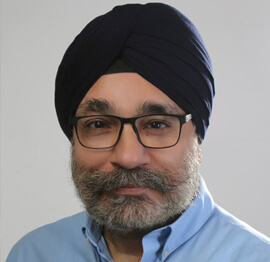
Subinder Khurana
Chief Architect StoryProcess, Founder NASSCOM DeepTech Club
Bryan Rishforth
Investor, Chairman Graphite
Bryn Everson
Director Biz Dev Graphite
Raj Tiwari
Digital Transformation Leader, Futurist and Visionary
Joseph Guadagno
Microsoft MVP, Lead Quicken Loans
Nikita Sachdev
Entrepreneur, Blockchain Enthusiast & Advisor, Social Media Influencer
Doug Wagner
COO & Founder Adapt Technical Group
Ritesh Modi
Architect, Senior Evangelist, Cloud Architect
Crystal Wenrick
Director Communications Mindcracker
Allen O’Neill
Microsoft MVP, Consulting Engineer/Architect
Praveen Kumar
CEO MCN Solutions
Chris Love
Founder Love2Dev, Microsoft MVP, Author
Sanjay Vyas
Microsoft Regional Director, Microsoft MVP, Founder & CEO SkillLabs Technologies
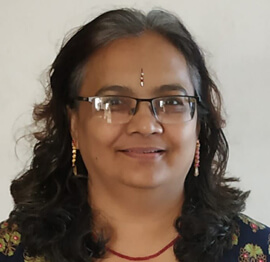
Veena Sarda
Deep Learning Consultant, Author
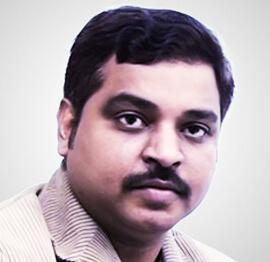
Sekhar Srinivasan
C# Corner MVP, Microsoft Certified Trainer, Pluralsight Author
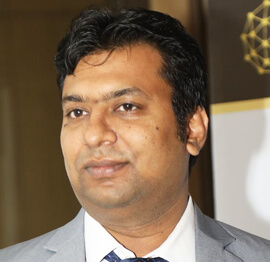
Lalit Bansal
Founder & CEO - EIY SYS
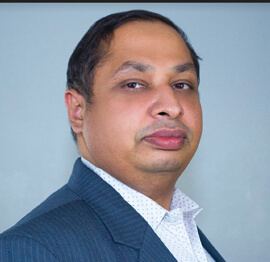
Navdeep Garg
CEO Revinfotech
Prakash Tripathi
Tech Manager/Leader, Microsoft MVP, Blogger
Bhavna Jain
Breakthrough Consultant
Naveen Sharma
Enterprise Architect, Leadership Coach, Author
Vidya Vrat Agarwal
Principal Architect, Microsoft MVP, Author
Sheetal Agarwal
Founder Clownselors, Medical Clown, Trainer
Abhishek Kant
Founder GTM Catalyst
Vishnu Saran
Founder & CEO VoiceQube
Sandeep Soni
Founder & CEO Deccansoft, Microsoft Certified Trainer
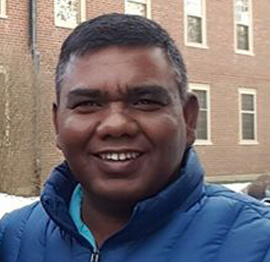
Parveen Malik
AVP InfoSec & Vulnerability Management, Information Security Expert
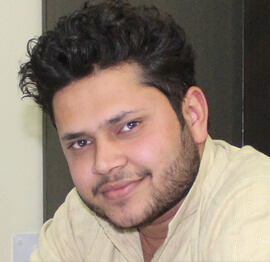
Nitin Pandit
Microsoft MVP, Developer Evangelist, Author
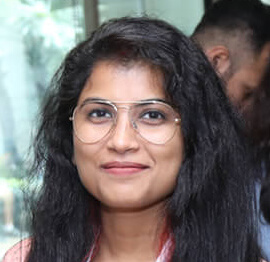
Niloshima Srivastava
C# Corner MVP, Tech Architect, Trainer, Blogger
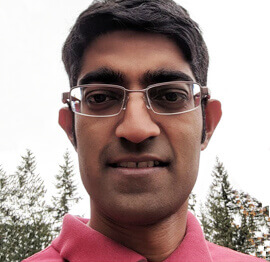
Bala Chirtsabesan
Senior Software Engineer at Microsoft, Author
Manoj Mittal
Sr. Technical Architect, C# Corner MVP, Author
Chandni Di
Co-Founder Voice of Slum
Vithal Wadje
Technical Lead, Microsoft MVP, Author
Shivam Ahuja
Founder SkillCircle, Business Mentor
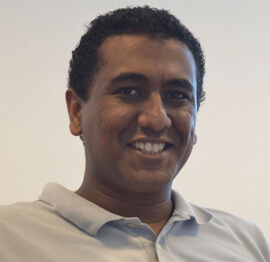
Chervine Bhiwoo
Solution Architect, Microsoft MVP, Author
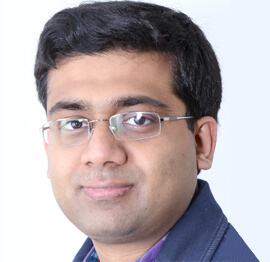
Saurabh Jain
Vice President Paytm, Founder Fun2Do Labs, Author
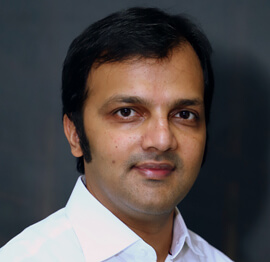
Vinay Solanki
Head IoT at Lenovo, Founder IoT-NCR
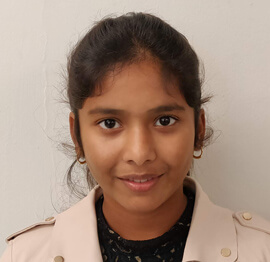
Anshu kumari
Founder Blockchainkids, Inventor, Trainer
Amit Singal
CEO Startup Buddy
Dev Pratap
Co-Founder & CEO Voice of Slum
Amey Vartak
Technology Consultant, Full Stack Developer, C# Corner MVP, Author
Viswanatha Swamy
Principal Software Engineer, C# Corner MVP, Author
Sanket Verma
Research Engineer @ Ballistics (Forensics) and Chair, PyData Delhi
Sourabh Somani
Lead Developer, Microsoft MVP, Author
Abhishek Mishra
Software Architect, C# Corner MVP, Author
Siddharth Vaghasia
Technical Consultant, C# Corner MVP, Blogger
Bassam Alugili
Senior Software Specialist, Database Expert
S Ravi Kumar
Solution Architect, C# Corner MVP, Author
Sundaram Subramanian
Full Stack Developer, C# Corner MVP, Speaker
Deepesh Somani
Solution Architect, Microsoft MVP, Author
Debasis Saha
Technical Project Manager, C# Corner MVP, Blogger, Author
Vipul Jain
Software Architect, C# Corner MVP, Author
Akshay Patel
Technical Architect, Microsoft Certified Trainer, C# Corner MVP, Author
Stephen Simon
RPA Developer, Evangelist, Author
Vivek Sharma
Founder Kingster636, AR/VR Specialist
Jeetendra Gund
Technical Lead, C# Corner MVP, Author
Sujal Beniwal
AI Enthusiast, Student
M Viknaraj
Microsoft MVP, Azure Architect, Author
Prasham Sabadra
Software Architect, C# Corner MVP, Trainer, Author
Aakash Maurya
Senior Developer, C# Corner MVP, Speaker
Ankit Sharma
Senior Software Engineer, C# Corner MVP, Author
Mangesh Gaherwar
Team Lead, C# Corner MVP, Author
Viral Jain
Technical Consultant, C# Corner MVP, Author
Bhasker Das
Solution Architect, Evangelist
Manish Dwivedi
Associate Project Manager
Ck Nitin
Programmer, Author
Rohit Gupta
Technical Trainer, Author
Manish Tewatia
Full-stack Marketer, UX Designer
Bhavya Gaur
Technical Illustrator
Rohit Tomar
SEO/SMO Expert
Web Track
Cloud & Data Track
Dev Track
Registration & Breakfast
Future of Desktop Apps with JS (ElectronJs)
Nitin Pandit
Building Serverless Microservices Using Microsoft Azure
Vithal Wadje
Innovating RPA: A Robot for Every Person
Stephen Simon
Managing Cloud Storage Accounts using Logic Apps
Viknaraj Manogararajah
Data visualization using Python
Sekhar Srinivasan
Going Cross platform with AR Foundation
Vivek Sharma
Keynote
Managing your Azure dependencies in ASP.NET Core apps using VS
Bala Chirtsabesan
Securing Applications on Intelligent Azure
Abhishek Mishra
Getting started with Blazor the Framework of Future
S Ravi Kumar
Lunch
Build Progressive Web Apps using Angular 9
Debasis Saha
Build and deploy to any platform using Azure DevOps
Chervine Bhiwoo
Deep Dive in Azure Service Bus
Akshay Patel
Build a Native Mobile Application using React Native and JavaScript
Joseph Guadagno
Making sense of Web Job, Web Job SDK and Functions in Azure
Prakash Tripathi
CloudFront Distribution in AWS
Viral Jain
Tea Break
Introduction to PowerBI
Aakash Maurya
Build Advanced SPFx solutions with React and Graph API
Siddharth Vaghasia
Build Business Intelligence Analyst (BIA) Skills
Sundaram Subramanian
Deep dive of Power Platform – AI BUILDER
Prasham Sabadra
Panel 1
What's new in SharePoint development
Vipul Jain
Build a SSO (Single Sign On) based Native JavaScript application with Microsoft Identity within 10 minutes
Manoj Mittal
Panel 2
Applications and working of AI
Veena Sarda
Deploying serverless API's with .Net core 3.0 on AWS & Azure
Amey Vartak
Panel 3
Blockchain with .NET Core (Ark)
Anshu Kumari
Closing Note & Prize Distribution
Dev Track
Cloud Track
Architecture Track
Emerging Tech Track
Registration & Breakfast
Creating Full-Stack Web Apps Using Server-Side Blazor
Ankit Sharma
Real time face recognition with MS Cognitive Services
Niloshima Srivastava
Building Scalable APIs with GraphQL
Jeetendra Gund
Future of development with AI and Blockchain
Navdeep Garg
Debugging Tips and Tricks with Visual Studio 2019
Joseph Guadagno
Azure Containers
Abhishek Kant
Enterprise Architecture
Naveen Sharma
Bot Framework - learn it fast and look like a boss!
Allen O’Neill
Keynote
.Net Core & C# 8 Performance
David McCarter
Working with Azure kubernetes services
Ritesh Modi
Becoming an Architect
Vidyavrat Agarwal
Why Techies Need to Learn Product Management
Saurabh Jain
Lunch
Build a rules engine in .Net Core
Sanjay Vyas
Building CI and CD Pipeline using Azure DevOps
Sandeep Soni
Entity Framework Core - Tips and Tricks, Performance Optimization, and Tuning
Bassam Alugili
Hacking your way into Data Science
Sanket Verma
Speed up your .Net Core Website
Sourabh Somani
Azure
Magnus Mårtensson
Demystifying Open Distro for Elasticsearch
Suman Debnath
Future of Data
Shivam Ahuja
Tea Break
gRPC with C# and .Net Core
Mangesh Gaherwar
Panel 1
Essentials of Cloud security
Parveen Malik
Power platform and Dynamics 365
Deepesh Somani
Microservices - the gRPC Way
Viswanatha Swamy
Panel 2
Reserved
Reserved
Closing Note & Prize Distribution
Rate limiting middleware for resilient ASP.NET Core APIs
Rate limiting controls how much traffic an API accepts over time. Creating a rate limiting middleware in ASP.NET Core prevents a sudden flood of requests from exhausting database connections, triggering excessive downstream charges, or turning a manageable spike into a full outage.
Effective protection depends on more than choosing a fixed requests-per-second value. The middleware needs explicit policies, fair caller identification, consistent counters across application instances, and clear responses that tell clients when to slow down.
Why uncontrolled traffic breaks APIs
Imagine a product catalogue endpoint receiving normal morning traffic, followed by a crawler that requests every item as quickly as possible. Without a limit, each request can open a database connection and occupy a worker thread. Response times rise, healthy users encounter errors, and recovery becomes harder as the backlog grows.
A rate limiter acts as a controlled entry point. It distinguishes legitimate usage from bursts that exceed an agreed budget, protecting both the API and its dependencies. It also provides a predictable mechanism for handling traffic during launches, promotions, billing cycles, or accidental retry loops.
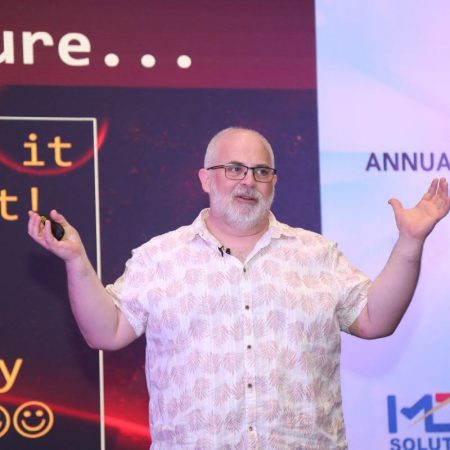
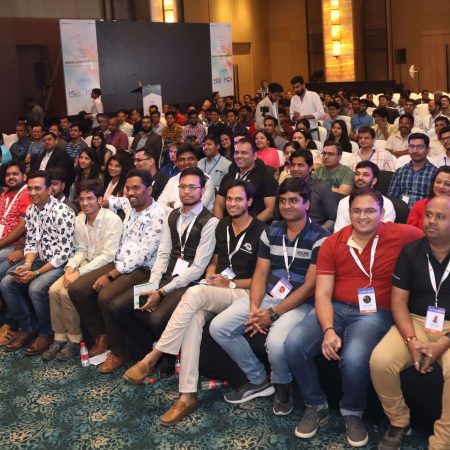
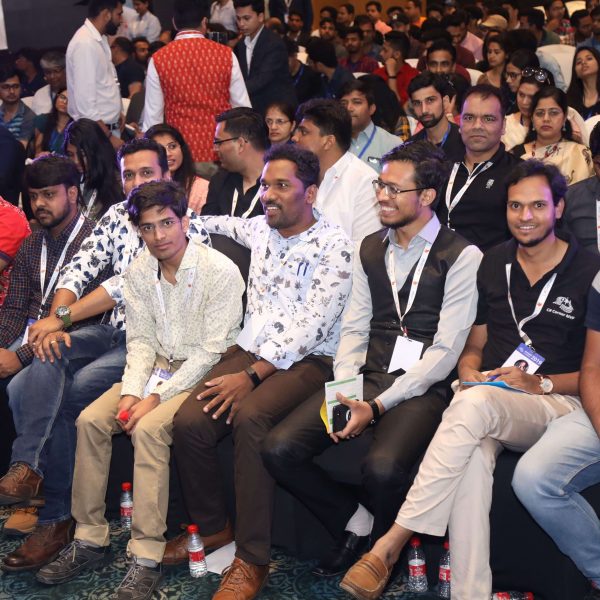
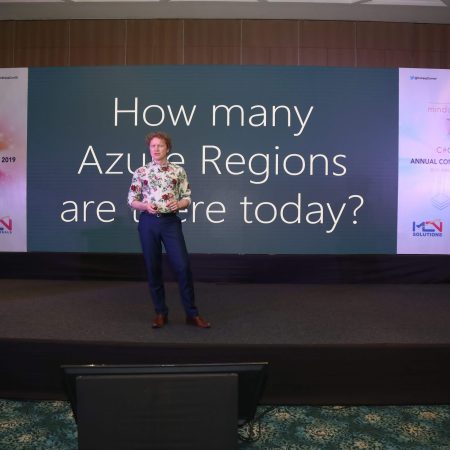
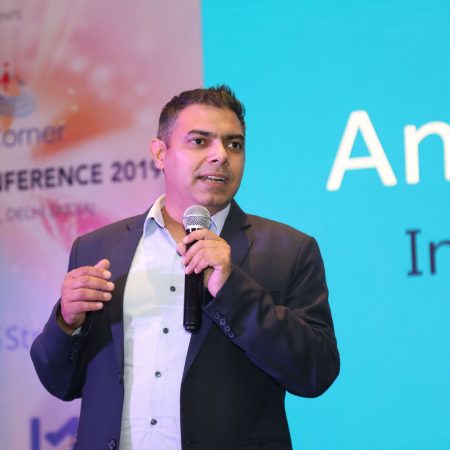
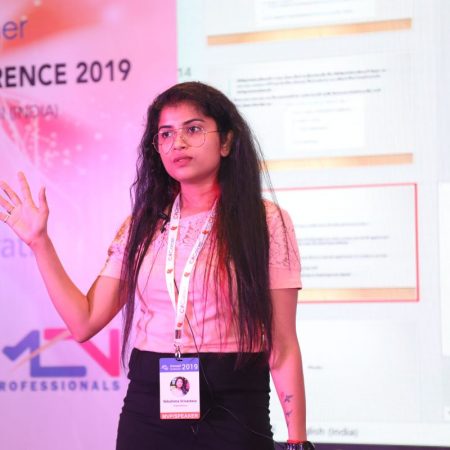
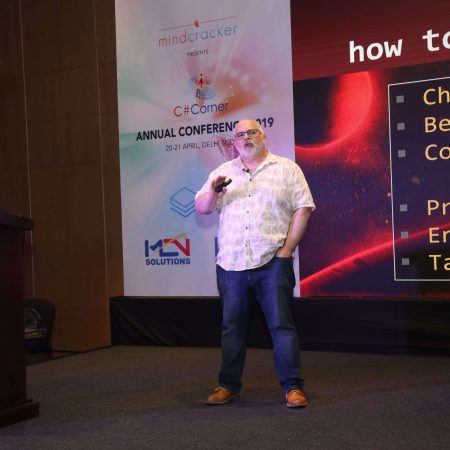
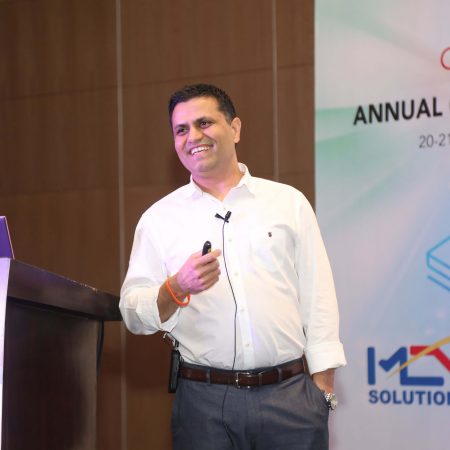
This API discipline belongs alongside the cloud, DevOps and data sessions at the C# Corner Annual Conference, where developers can examine platform decisions alongside the operational constraints of production services.
Designing policies that match actual demand
Group endpoints by their cost and usage pattern. Read-only catalogue requests can usually tolerate more traffic than an export that runs an expensive report. Authentication and password-reset endpoints often need tighter controls because repeated attempts can indicate credential abuse. A single global limit for every route is simpler, but it can unnecessarily restrict low-risk operations.
Choose an algorithm that reflects the intended behaviour. A fixed window provides a simple quota but permits a burst around each window boundary. A sliding window spreads limits across time. A token bucket allows controlled bursts while enforcing an average rate, and a concurrency limiter directly controls how many operations may run simultaneously.
Set initial thresholds from measured traffic, not intuition alone. Observe normal traffic during Australian business hours, including an arvo release when teams across Melbourne and Sydney might begin broad testing. Then add enough headroom for genuine demand. Review the limits when customer patterns change, since a quota that suited a small pilot may be wasteful for a national product.
Building the middleware into the request pipeline
Register the middleware after routing so it can inspect the selected endpoint. When policies depend on authenticated users, place it after authentication; otherwise, the available identity may be incomplete. Middleware order matters because an early rejection should avoid work that the caller was never authorised to request.
Separate policy evaluation from counter storage through an interface such as IRateLimitStore. The store acquires capacity and returns an allowed flag, any remaining quota, and a retry delay when appropriate. A compact version of the middleware can then remain focused on the HTTP request and response:
public sealed class RateLimitMiddleware
{
    private readonly RequestDelegate _next;
    private readonly IRateLimitStore _store;

    public RateLimitMiddleware(RequestDelegate next, IRateLimitStore store)
    {
        _next = next;
        _store = store;
    }

    public async Task InvokeAsync(HttpContext context)
    {
        var key = context.Request.Path.Value ?? "/";
        var decision = await _store.TryAcquireAsync(
            key, context.RequestAborted);

        if (!decision.Allowed)
        {
            context.Response.StatusCode = StatusCodes.Status429TooManyRequests;
            context.Response.Headers.RetryAfter =
                decision.RetryAfterSeconds.ToString();

            await context.Response.WriteAsJsonAsync(
                new { error = "Too many requests." },
                context.RequestAborted);
            return;
        }

        await _next(context);
    }
}
The path-only key is deliberately simple. A multi-tenant application would normally incorporate a tenant identifier, account, or authorised user before calling the store. That key construction must be deterministic and resistant to attackers creating unlimited identities.
Return HTTP 429 for a rejected request and include Retry-After when the server can estimate the wait. Keep the response body consistent, and avoid exposing internal quota details that reveal other customers’ activity. The store must perform atomic acquisition; a read followed by an unchecked increment can over-admit requests under concurrent load.
Keeping counters consistent across multiple instances
An in-memory counter is fast, but each application instance maintains a separate allowance. A service running on four servers can therefore accept roughly four times the intended traffic. This becomes particularly noticeable during autoscaling, when a traffic surge creates additional instances and silently expands the limit.
Use a shared store such as Redis when limits must apply across the service. Atomic scripts or equivalent server-side operations can update counters safely, while expiry prevents abandoned keys from consuming memory indefinitely. The latency and operational cost of that store must remain acceptable for the endpoint’s traffic.
For teams in Sydney, Melbourne, Brisbane or Perth, place regional infrastructure close to the application while checking contractual and data-residency requirements. Azure Australia East and Australia Southeast are common regional choices for Australian workloads, but users in Perth can still experience additional round-trip time against east-coast services. Budget Redis and related resources in Australian dollars, remembering that GST generally applies to taxable business purchases.
Decide how the service behaves if the shared store becomes unavailable. A public read endpoint may fail open and continue serving cached data, while an expensive report might fail closed. Apply that decision per policy rather than placing one global fallback over every route.
Identifying callers without penalising the wrong people
A fair limit needs a stable caller identity. For business users, a tenant or account identifier is usually more meaningful than an IP address. For service-to-service traffic, use the authenticated client identifier. Anonymous callers may require an IP-based partition, ideally combined with a coarse route category to prevent one address from consuming another endpoint’s allowance.
Do not trust identity values that have not been validated by the authentication pipeline. Middleware ordering becomes critical here: a user identifier is empty when authentication runs later, while claims copied directly from an untrusted header could let callers manufacture fresh identities. Resolve identity from the server’s authenticated principal or trusted endpoint metadata.
IP addresses also need careful interpretation. Many Australian households connect through the NBN, and some addresses change when their connection is reallocated. Mobile networks commonly use carrier-grade NAT, placing numerous unrelated customers behind one public address. A strict per-address limit can therefore block a university, corporate office, or mobile carrier customer collectively. Use appropriate prefixes, supplement IP identity with authenticated context, and ensure clients can request a legitimate increase.
Comparing the main enforcement approaches
Modern ASP.NET Core includes built-in rate limiting policies for fixed windows, token buckets, and concurrency. Named policies can partition requests by endpoint, IP address, or authenticated user. This is often the best starting point, although the default rejection callback must be configured to return the intended status rather than assuming every rejection automatically produces a 429 response.
A custom middleware remains useful when quotas depend on subscription tiers, weighted operations, multiple resources, or a business-specific retry calculation. An API gateway provides broader protection across an estate, while a service mesh can apply consistent limits between services. These layers operate at different boundaries, so their responsibilities should not overlap unintentionally.
| Approach | Best fit | Main advantages | Main trade-offs |
|---|---|---|---|
| Built-in ASP.NET Core limiter | Standard endpoint and user quotas | Fast adoption, familiar policies, dependency injection | Less freedom for complex business rules |
| Custom middleware | Tenant tiers and specialised quotas | Precise control over keys, responses, and algorithms | You maintain the implementation and its tests |
| Redis-backed custom limiter | Limits shared across instances | Consistent distributed counters | Network latency and operational overhead |
| API gateway or service mesh | Uniform protection across services | Broad enforcement and centralised visibility | Additional infrastructure and less application context |
The practical choice depends on where the authoritative quota belongs. Standard platform policies suit consistent service-wide rules, while custom application logic suits entitlements and resource consumption. A gateway can remain the coarse outer boundary as the application applies finer-grained limits.
Rolling out safely and proving the behaviour
Introduce enforcement in stages. Begin by calculating decisions without rejecting requests, allowing teams to compare projected limits with actual traffic. Then apply a generous threshold to a low-risk endpoint, followed by stricter policies for authentication, exports, or high-cost operations. Keep each change observable and reversible.
Exercise normal traffic, deliberate bursts, concurrent requests, expired counters, and failures of the backing store. Confirm that legitimate clients receive 429 responses with useful retry guidance, while permitted requests continue without added latency. Track rejection counts, acquisition time, store errors, and the distribution of active keys; excessive key cardinality can itself become a performance problem.
The finished limiter should enforce the same budget across every instance, distinguish callers fairly, and fail in a deliberate manner when its dependencies are impaired. A predictable API protects its downstream systems while giving legitimate clients a clear path to the resources they need.
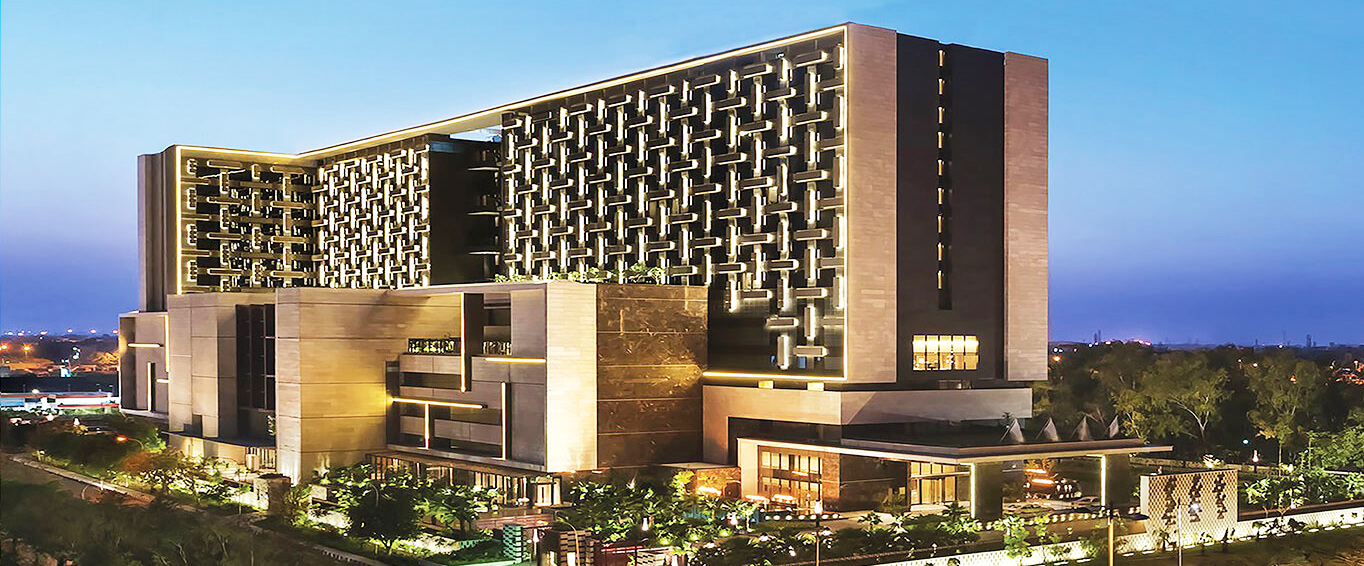
1, CBD, Maharaj Surajmal Road, Near Yamuna Sports Complex, Delhi, 110032
GENERAL QUERIES
Manish Tewatia
manish@csharpcon.com
+91-9718-431-042
TICKET QUERIES
Atul Gupta
conference@csharpcon.com
+91-9910-125-804