Presents
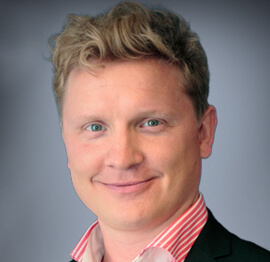
Magnus Mårtensson
Microsoft Regional Director, Azure MVP, CEO Loftysoft
Avirag Jain
Director & CTO R Systems
Mahesh Chand
Founder C# Corner, CEO Mindcracker
Chris Gali
CEO & Co-Founder Graphite
Subinder Khurana
Chief Architect StoryProcess, Founder NASSCOM DeepTech Club
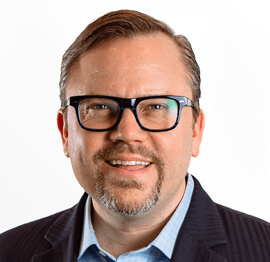
Bryan Rishforth
Investor, Chairman Graphite
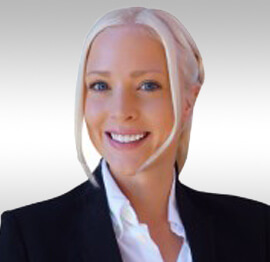
Bryn Everson
Director Biz Dev Graphite
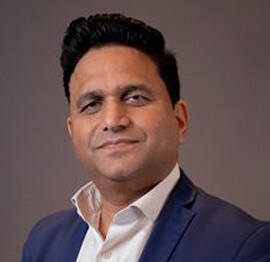
Raj Tiwari
Digital Transformation Leader, Futurist and Visionary
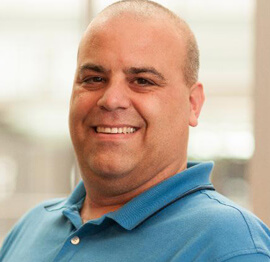
Joseph Guadagno
Microsoft MVP, Lead Quicken Loans
Nikita Sachdev
Entrepreneur, Blockchain Enthusiast & Advisor, Social Media Influencer
Doug Wagner
COO & Founder Adapt Technical Group
Ritesh Modi
Architect, Senior Evangelist, Cloud Architect
Crystal Wenrick
Director Communications Mindcracker
Allen O’Neill
Microsoft MVP, Consulting Engineer/Architect
Praveen Kumar
CEO MCN Solutions
Chris Love
Founder Love2Dev, Microsoft MVP, Author
Sanjay Vyas
Microsoft Regional Director, Microsoft MVP, Founder & CEO SkillLabs Technologies
Veena Sarda
Deep Learning Consultant, Author
Sekhar Srinivasan
C# Corner MVP, Microsoft Certified Trainer, Pluralsight Author
Lalit Bansal
Founder & CEO - EIY SYS
Navdeep Garg
CEO Revinfotech
Prakash Tripathi
Tech Manager/Leader, Microsoft MVP, Blogger
Bhavna Jain
Breakthrough Consultant
Naveen Sharma
Enterprise Architect, Leadership Coach, Author
Vidya Vrat Agarwal
Principal Architect, Microsoft MVP, Author
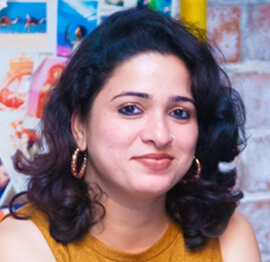
Sheetal Agarwal
Founder Clownselors, Medical Clown, Trainer
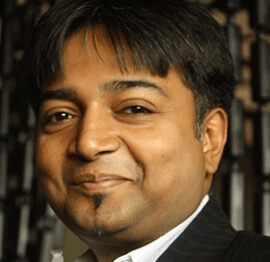
Abhishek Kant
Founder GTM Catalyst
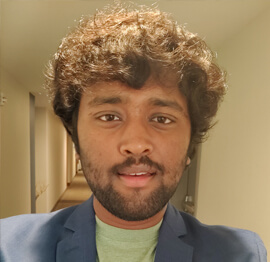
Vishnu Saran
Founder & CEO VoiceQube
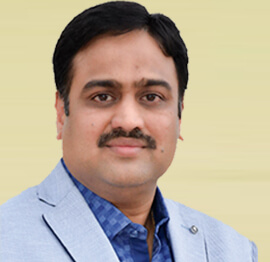
Sandeep Soni
Founder & CEO Deccansoft, Microsoft Certified Trainer
Parveen Malik
AVP InfoSec & Vulnerability Management, Information Security Expert
Nitin Pandit
Microsoft MVP, Developer Evangelist, Author
Niloshima Srivastava
C# Corner MVP, Tech Architect, Trainer, Blogger
Bala Chirtsabesan
Senior Software Engineer at Microsoft, Author
Manoj Mittal
Sr. Technical Architect, C# Corner MVP, Author
Chandni Di
Co-Founder Voice of Slum
Vithal Wadje
Technical Lead, Microsoft MVP, Author
Shivam Ahuja
Founder SkillCircle, Business Mentor
Chervine Bhiwoo
Solution Architect, Microsoft MVP, Author
Saurabh Jain
Vice President Paytm, Founder Fun2Do Labs, Author
Vinay Solanki
Head IoT at Lenovo, Founder IoT-NCR
Anshu kumari
Founder Blockchainkids, Inventor, Trainer
Amit Singal
CEO Startup Buddy
Dev Pratap
Co-Founder & CEO Voice of Slum
Amey Vartak
Technology Consultant, Full Stack Developer, C# Corner MVP, Author
Viswanatha Swamy
Principal Software Engineer, C# Corner MVP, Author
Sanket Verma
Research Engineer @ Ballistics (Forensics) and Chair, PyData Delhi
Sourabh Somani
Lead Developer, Microsoft MVP, Author
Abhishek Mishra
Software Architect, C# Corner MVP, Author
Siddharth Vaghasia
Technical Consultant, C# Corner MVP, Blogger
Bassam Alugili
Senior Software Specialist, Database Expert
S Ravi Kumar
Solution Architect, C# Corner MVP, Author
Sundaram Subramanian
Full Stack Developer, C# Corner MVP, Speaker
Deepesh Somani
Solution Architect, Microsoft MVP, Author
Debasis Saha
Technical Project Manager, C# Corner MVP, Blogger, Author
Vipul Jain
Software Architect, C# Corner MVP, Author
Akshay Patel
Technical Architect, Microsoft Certified Trainer, C# Corner MVP, Author
Stephen Simon
RPA Developer, Evangelist, Author
Vivek Sharma
Founder Kingster636, AR/VR Specialist
Jeetendra Gund
Technical Lead, C# Corner MVP, Author
Sujal Beniwal
AI Enthusiast, Student
M Viknaraj
Microsoft MVP, Azure Architect, Author
Prasham Sabadra
Software Architect, C# Corner MVP, Trainer, Author
Aakash Maurya
Senior Developer, C# Corner MVP, Speaker
Ankit Sharma
Senior Software Engineer, C# Corner MVP, Author
Mangesh Gaherwar
Team Lead, C# Corner MVP, Author
Viral Jain
Technical Consultant, C# Corner MVP, Author
Bhasker Das
Solution Architect, Evangelist
Manish Dwivedi
Associate Project Manager
Ck Nitin
Programmer, Author
Rohit Gupta
Technical Trainer, Author
Manish Tewatia
Full-stack Marketer, UX Designer
Bhavya Gaur
Technical Illustrator
Rohit Tomar
SEO/SMO Expert
Web Track
Cloud & Data Track
Dev Track
Registration & Breakfast
Future of Desktop Apps with JS (ElectronJs)
Nitin Pandit
Building Serverless Microservices Using Microsoft Azure
Vithal Wadje
Innovating RPA: A Robot for Every Person
Stephen Simon
Managing Cloud Storage Accounts using Logic Apps
Viknaraj Manogararajah
Data visualization using Python
Sekhar Srinivasan
Going Cross platform with AR Foundation
Vivek Sharma
Keynote
Managing your Azure dependencies in ASP.NET Core apps using VS
Bala Chirtsabesan
Securing Applications on Intelligent Azure
Abhishek Mishra
Getting started with Blazor the Framework of Future
S Ravi Kumar
Lunch
Build Progressive Web Apps using Angular 9
Debasis Saha
Build and deploy to any platform using Azure DevOps
Chervine Bhiwoo
Deep Dive in Azure Service Bus
Akshay Patel
Build a Native Mobile Application using React Native and JavaScript
Joseph Guadagno
Making sense of Web Job, Web Job SDK and Functions in Azure
Prakash Tripathi
CloudFront Distribution in AWS
Viral Jain
Tea Break
Introduction to PowerBI
Aakash Maurya
Build Advanced SPFx solutions with React and Graph API
Siddharth Vaghasia
Build Business Intelligence Analyst (BIA) Skills
Sundaram Subramanian
Deep dive of Power Platform – AI BUILDER
Prasham Sabadra
Panel 1
What's new in SharePoint development
Vipul Jain
Build a SSO (Single Sign On) based Native JavaScript application with Microsoft Identity within 10 minutes
Manoj Mittal
Panel 2
Applications and working of AI
Veena Sarda
Deploying serverless API's with .Net core 3.0 on AWS & Azure
Amey Vartak
Panel 3
Blockchain with .NET Core (Ark)
Anshu Kumari
Closing Note & Prize Distribution
Dev Track
Cloud Track
Architecture Track
Emerging Tech Track
Registration & Breakfast
Creating Full-Stack Web Apps Using Server-Side Blazor
Ankit Sharma
Real time face recognition with MS Cognitive Services
Niloshima Srivastava
Building Scalable APIs with GraphQL
Jeetendra Gund
Future of development with AI and Blockchain
Navdeep Garg
Debugging Tips and Tricks with Visual Studio 2019
Joseph Guadagno
Azure Containers
Abhishek Kant
Enterprise Architecture
Naveen Sharma
Bot Framework - learn it fast and look like a boss!
Allen O’Neill
Keynote
.Net Core & C# 8 Performance
David McCarter
Working with Azure kubernetes services
Ritesh Modi
Becoming an Architect
Vidyavrat Agarwal
Why Techies Need to Learn Product Management
Saurabh Jain
Lunch
Build a rules engine in .Net Core
Sanjay Vyas
Building CI and CD Pipeline using Azure DevOps
Sandeep Soni
Entity Framework Core - Tips and Tricks, Performance Optimization, and Tuning
Bassam Alugili
Hacking your way into Data Science
Sanket Verma
Speed up your .Net Core Website
Sourabh Somani
Azure
Magnus Mårtensson
Demystifying Open Distro for Elasticsearch
Suman Debnath
Future of Data
Shivam Ahuja
Tea Break
gRPC with C# and .Net Core
Mangesh Gaherwar
Panel 1
Essentials of Cloud security
Parveen Malik
Power platform and Dynamics 365
Deepesh Somani
Microservices - the gRPC Way
Viswanatha Swamy
Panel 2
Reserved
Reserved
Closing Note & Prize Distribution
How To Test ASP.NET Core Filters With TestServer
ASP.NET Core filters sit close to the HTTP boundary, where controller selection, authorization, model validation, exception handling, and result execution meet. A unit test that calls a filter method directly can verify a small branch, yet it may miss the registration, middleware, routing, and response behaviour that users actually experience.
TestServer provides a useful middle ground. It runs an in-memory ASP.NET Core application and lets tests send real HttpRequestMessage instances without opening a network port. This makes it suitable for checking filter behaviour through the framework pipeline while keeping tests faster and more controlled than tests against a deployed environment.
Why Filters Need Focused Integration Tests
An ASP.NET Core filter can implement IAsyncActionFilter, IActionFilter, IAsyncAuthorizationFilter, IExceptionFilter, or a resource and result filter interface. Its outcome can depend on dependency injection, endpoint metadata, model state, route values, authentication claims, and the order in which MVC invokes other components.
For example, an authorization filter may short-circuit a request with a 403 Forbidden result. A validation filter might return a structured 400 Bad Request response, while an exception filter could translate a domain exception into 409 Conflict. Calling the filter with a hand-built ActionExecutingContext checks its internal code, but it does not prove that the filter is attached to the intended controller or that its response is serialised correctly.
A TestServer test should therefore focus on observable behaviour: the request sent, the status code returned, headers, response body, and whether the downstream action ran. This approach is particularly valuable in larger Australian development teams where a shared API may be maintained in Sydney, Melbourne, Brisbane, or Perth and small registration changes can affect multiple services.
Build A Minimal TestServer Host
Create a test project that references the application project and uses Microsoft.AspNetCore.TestHost. For modern ASP.NET Core applications, a small WebApplicationBuilder can host the controllers and filter registrations directly inside the test. The application under test should use the same service registration path as production wherever practical.
A minimal setup can look like this:
using Microsoft.AspNetCore.Hosting;
using Microsoft.AspNetCore.Mvc.Testing;
using Microsoft.AspNetCore.TestHost;

public sealed class ApiFixture : WebApplicationFactory<Program>
{
    protected override void ConfigureWebHost(IWebHostBuilder builder)
    {
        builder.UseTestServer();

        builder.ConfigureServices(services =>
        {
            // Replace external services with deterministic test doubles.
        });
    }
}
If the application uses top-level statements, make Program visible to the test assembly with public partial class Program { }. The fixture can then create an HttpClient, and each test can send requests through the in-memory server. Avoid replacing the filter itself unless the purpose of the test is to verify another component; replacing it would remove the behaviour under examination.
External resources should be controlled at the host boundary. Substitute repositories, message buses, clocks, and identity providers with fakes or mocks. Database tests can use a dedicated test database where persistence behaviour matters, but a filter test should not fail because a developer’s local SQL Server is unavailable.
Send Requests Through The MVC Pipeline
A useful test controller should expose a small, explicit endpoint. For example, an action decorated with [ServiceFilter(typeof(TenantFilter))] can return a tenant-specific payload. The test client then sends a request containing the header or claim that the filter expects.
[Fact]
public async Task Missing_tenant_header_returns_bad_request()
{
    await using var factory = new ApiFixture();
    using var client = factory.CreateClient();

    using var response = await client.GetAsync("/orders");

    Assert.Equal(HttpStatusCode.BadRequest, response.StatusCode);
    var body = await response.Content.ReadAsStringAsync();
    Assert.Contains("tenant", body, StringComparison.OrdinalIgnoreCase);
}
The test is stronger than a direct method invocation because routing, filter discovery, dependency injection, and response formatting all participate. Add a second test with a valid header and assert that the action returns its expected result. If the filter is intended to stop the action, inject a spy service or expose an observable fake and assert that the action-side operation was never performed.
Headers and claims should be created in the same shape as production. For authenticated paths, configure a test authentication handler rather than manually setting an Authorization header that no registered scheme understands. The handler can return a ClaimsPrincipal with roles, scopes, or tenant identifiers, allowing tests to cover both accepted and rejected identities.
Choose The Right Test Boundary
TestServer is most effective when the question concerns an HTTP-visible result. Direct unit tests remain useful for complex filter algorithms, especially when many edge cases can be evaluated without routing or serialisation. The two styles answer different questions and should sit beside each other rather than compete.
| Test approach | Best use | Main strength | Typical limitation |
|---|---|---|---|
| Direct filter unit test | Branches and dependency interactions | Very fast and precise | Does not verify MVC registration |
| TestServer request test | Status codes and pipeline behaviour | Exercises routing, DI, filters, and formatting | Requires a host and more setup |
| Full end-to-end test | Deployment and infrastructure confidence | Represents a near-real environment | Slower and harder to isolate |
| Contract test | Client-facing response compatibility | Protects API agreements | Needs maintained contracts and fixtures |
A practical suite might use direct tests for exception mapping and TestServer tests for filter ordering, endpoint selection, and response contracts. Keep the number of full environment tests smaller, reserving them for concerns such as reverse proxies, TLS termination, Azure configuration, or deployed authentication.
This boundary also helps with Australian privacy obligations. If a filter removes personal information from error responses under the Privacy Act 1988, a TestServer test can assert that names, addresses, or Medicare-related identifiers do not appear in the payload without loading real customer data. Synthetic fixtures are safer and easier to run in shared CI environments.
Test Authorization And Short-Circuiting
Authorization filters deserve separate cases for anonymous users, authenticated users without the required permission, and users with the correct policy or role. Configure a test scheme in the host:
builder.ConfigureTestServices(services =>
{
    services.AddAuthentication("Test")
        .AddScheme<AuthenticationSchemeOptions, TestAuthHandler>(
            "Test", _ => { });
});
The handler can read a custom test header and create the desired claims. Each test then sends a request such as X-Test-Role: finance-reader. Assert the complete result: status code, WWW-Authenticate header where applicable, and response body. A 401 means authentication was missing or rejected; a 403 means the identity was recognised but lacked permission.
Short-circuiting should be tested explicitly. A filter that rejects a request must prevent the action and later filters from running. A fake command handler with a call counter makes this visible. This matters in payment, payroll, and government-related systems, where an incorrectly ordered filter could allow a side effect before authorization completes.
When filters depend on retries or transient data access, keep the concerns separate. The filter test should verify how the filter reacts to a success, timeout, or known exception; database resiliency belongs in its own suite. A focused retry policy guide can inform those persistence tests without making every HTTP test wait for retry delays.
Verify Exceptions And Result Formatting
Exception filters should be tested with a deliberately failing dependency. Register a fake service that throws a known domain exception, send a request to the relevant action, and assert the mapped status code and problem-details payload. Also test an unexpected exception if the application has a safe generic handler; the response should avoid stack traces and internal connection details.
Do not assert the entire JSON string unless exact formatting is part of the contract. Deserialize the response into ProblemDetails or a project-specific error model and check stable fields such as Status, Title, Type, and a correlation identifier. This reduces failures when property ordering or harmless whitespace changes.
Result filters require attention to headers and content negotiation. Send requests with different Accept values when the filter changes the response representation, and verify cache, correlation, or security headers with case-insensitive lookups. If the filter appends a header, test that it appears once; repeated execution or incorrect registration can otherwise produce duplicate values that are difficult to spot in manual testing.
Keep TestServer Suites Reliable
Create a fresh client for tests that modify authentication, headers, or service registrations. A shared fixture is efficient, but mutable state can leak between tests. Use unique identifiers, reset fake repositories between cases, and avoid relying on execution order. Parallel test execution should remain enabled unless the application has a clearly isolated reason to disable it.
Time-dependent filters should receive an injectable clock. Replace DateTime.UtcNow with an IClock or equivalent abstraction and set a fixed instant in the test. The same principle applies to generated correlation IDs, feature flags, and external API responses. Deterministic inputs make failures reproducible on a developer laptop and in a hosted CI runner.
Australian teams often run builds across AEST, ACST, and AWST environments, with daylight-saving changes affecting New South Wales, Victoria, Queensland, South Australia, and Western Australia differently. Use UTC in application assertions and configure test culture explicitly when dates, decimal values, or validation messages are involved. This prevents a filter test from passing in Brisbane but failing on a Melbourne workstation after a daylight-saving transition.
Diagnose Failures Without Guesswork
When a TestServer request returns an unexpected result, first inspect the route and status code, then log the response body and registered authentication scheme. A 404 often indicates endpoint mapping rather than filter logic; a 401 can mean the test handler was never selected; a 500 may reveal a missing service registration. These distinctions shorten debugging considerably.
Use a named test category or trait for filter pipeline tests, and keep their fixtures close to the API project. Run them on every pull request because they are usually quick enough for ordinary developer workflows. More expensive database or deployed-environment tests can run in a separate pipeline stage without reducing feedback from the core filter suite.
A dependable set of TestServer tests proves the behaviour that matters at the HTTP boundary: the right filter is registered, the request reaches the expected endpoint, rejected requests stop safely, accepted requests continue, exceptions become intentional responses, and sensitive data stays out of the payload. That evidence gives ASP.NET Core teams a stable foundation for changing controllers, authentication, and infrastructure without silently weakening the request pipeline.
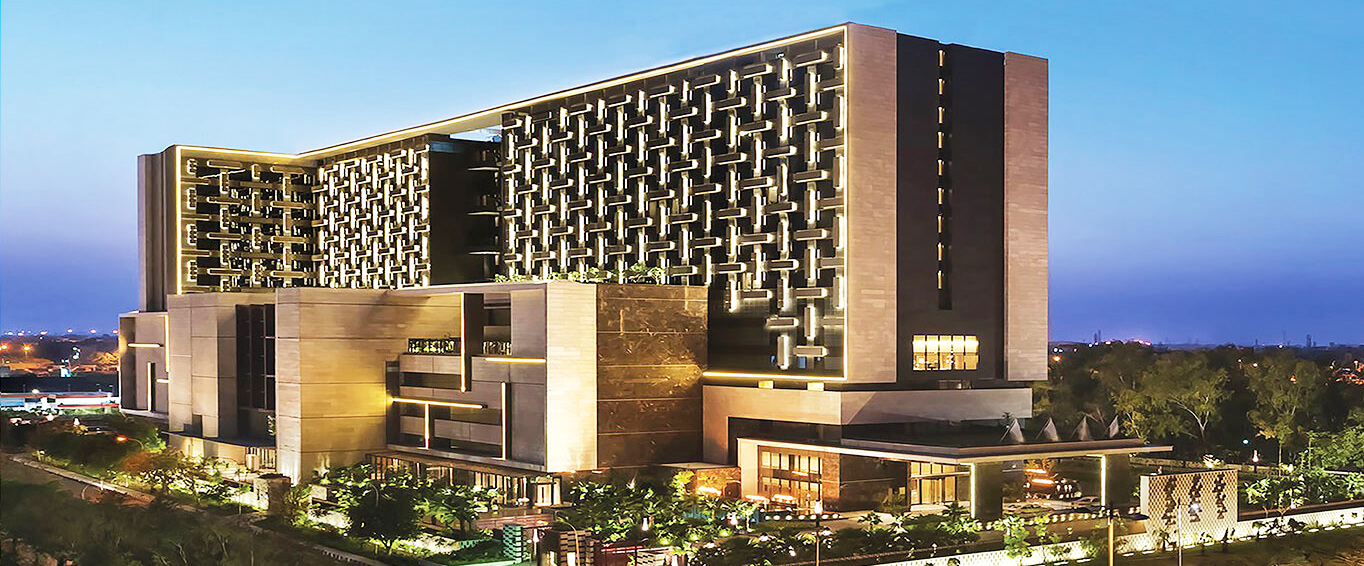
1, CBD, Maharaj Surajmal Road, Near Yamuna Sports Complex, Delhi, 110032
GENERAL QUERIES
Manish Tewatia
manish@csharpcon.com
+91-9718-431-042
TICKET QUERIES
Atul Gupta
conference@csharpcon.com
+91-9910-125-804