Presents
Magnus Mårtensson
Microsoft Regional Director, Azure MVP, CEO Loftysoft
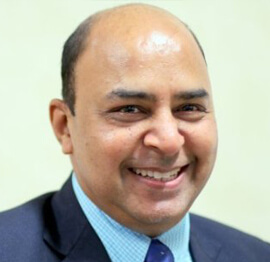
Avirag Jain
Director & CTO R Systems
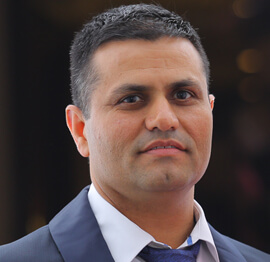
Mahesh Chand
Founder C# Corner, CEO Mindcracker
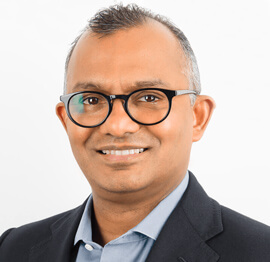
Chris Gali
CEO & Co-Founder Graphite
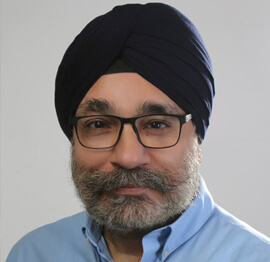
Subinder Khurana
Chief Architect StoryProcess, Founder NASSCOM DeepTech Club
Bryan Rishforth
Investor, Chairman Graphite
Bryn Everson
Director Biz Dev Graphite
Raj Tiwari
Digital Transformation Leader, Futurist and Visionary
Joseph Guadagno
Microsoft MVP, Lead Quicken Loans
Nikita Sachdev
Entrepreneur, Blockchain Enthusiast & Advisor, Social Media Influencer
Doug Wagner
COO & Founder Adapt Technical Group
Ritesh Modi
Architect, Senior Evangelist, Cloud Architect
Crystal Wenrick
Director Communications Mindcracker
Allen O’Neill
Microsoft MVP, Consulting Engineer/Architect
Praveen Kumar
CEO MCN Solutions
Chris Love
Founder Love2Dev, Microsoft MVP, Author
Sanjay Vyas
Microsoft Regional Director, Microsoft MVP, Founder & CEO SkillLabs Technologies
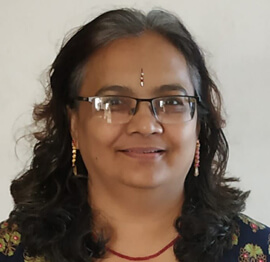
Veena Sarda
Deep Learning Consultant, Author
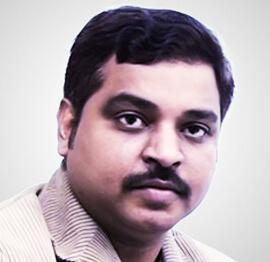
Sekhar Srinivasan
C# Corner MVP, Microsoft Certified Trainer, Pluralsight Author
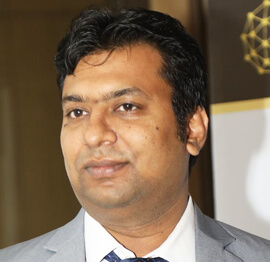
Lalit Bansal
Founder & CEO - EIY SYS
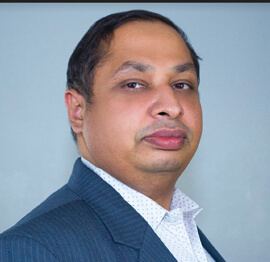
Navdeep Garg
CEO Revinfotech
Prakash Tripathi
Tech Manager/Leader, Microsoft MVP, Blogger
Bhavna Jain
Breakthrough Consultant
Naveen Sharma
Enterprise Architect, Leadership Coach, Author
Vidya Vrat Agarwal
Principal Architect, Microsoft MVP, Author
Sheetal Agarwal
Founder Clownselors, Medical Clown, Trainer
Abhishek Kant
Founder GTM Catalyst
Vishnu Saran
Founder & CEO VoiceQube
Sandeep Soni
Founder & CEO Deccansoft, Microsoft Certified Trainer
Parveen Malik
AVP InfoSec & Vulnerability Management, Information Security Expert
Nitin Pandit
Microsoft MVP, Developer Evangelist, Author
Niloshima Srivastava
C# Corner MVP, Tech Architect, Trainer, Blogger
Bala Chirtsabesan
Senior Software Engineer at Microsoft, Author
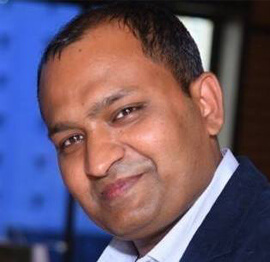
Manoj Mittal
Sr. Technical Architect, C# Corner MVP, Author
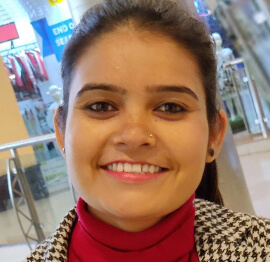
Chandni Di
Co-Founder Voice of Slum
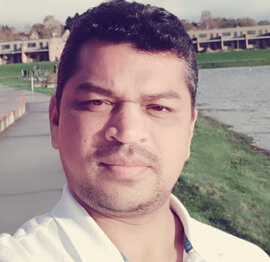
Vithal Wadje
Technical Lead, Microsoft MVP, Author
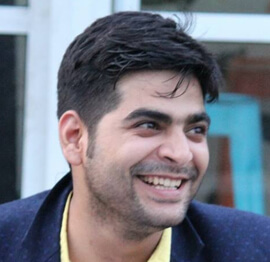
Shivam Ahuja
Founder SkillCircle, Business Mentor
Chervine Bhiwoo
Solution Architect, Microsoft MVP, Author
Saurabh Jain
Vice President Paytm, Founder Fun2Do Labs, Author
Vinay Solanki
Head IoT at Lenovo, Founder IoT-NCR
Anshu kumari
Founder Blockchainkids, Inventor, Trainer
Amit Singal
CEO Startup Buddy
Dev Pratap
Co-Founder & CEO Voice of Slum
Amey Vartak
Technology Consultant, Full Stack Developer, C# Corner MVP, Author
Viswanatha Swamy
Principal Software Engineer, C# Corner MVP, Author
Sanket Verma
Research Engineer @ Ballistics (Forensics) and Chair, PyData Delhi
Sourabh Somani
Lead Developer, Microsoft MVP, Author
Abhishek Mishra
Software Architect, C# Corner MVP, Author
Siddharth Vaghasia
Technical Consultant, C# Corner MVP, Blogger
Bassam Alugili
Senior Software Specialist, Database Expert
S Ravi Kumar
Solution Architect, C# Corner MVP, Author
Sundaram Subramanian
Full Stack Developer, C# Corner MVP, Speaker
Deepesh Somani
Solution Architect, Microsoft MVP, Author
Debasis Saha
Technical Project Manager, C# Corner MVP, Blogger, Author
Vipul Jain
Software Architect, C# Corner MVP, Author
Akshay Patel
Technical Architect, Microsoft Certified Trainer, C# Corner MVP, Author
Stephen Simon
RPA Developer, Evangelist, Author
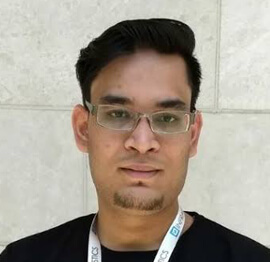
Vivek Sharma
Founder Kingster636, AR/VR Specialist
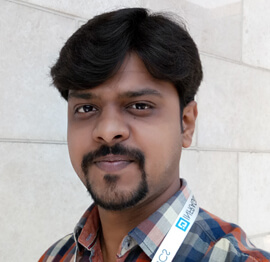
Jeetendra Gund
Technical Lead, C# Corner MVP, Author
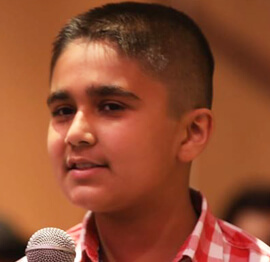
Sujal Beniwal
AI Enthusiast, Student
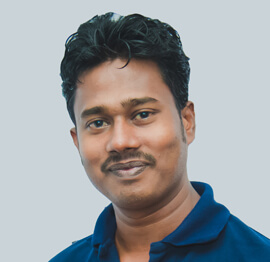
M Viknaraj
Microsoft MVP, Azure Architect, Author
Prasham Sabadra
Software Architect, C# Corner MVP, Trainer, Author
Aakash Maurya
Senior Developer, C# Corner MVP, Speaker
Ankit Sharma
Senior Software Engineer, C# Corner MVP, Author
Mangesh Gaherwar
Team Lead, C# Corner MVP, Author
Viral Jain
Technical Consultant, C# Corner MVP, Author
Bhasker Das
Solution Architect, Evangelist
Manish Dwivedi
Associate Project Manager
Ck Nitin
Programmer, Author
Rohit Gupta
Technical Trainer, Author
Manish Tewatia
Full-stack Marketer, UX Designer
Bhavya Gaur
Technical Illustrator
Rohit Tomar
SEO/SMO Expert
Web Track
Cloud & Data Track
Dev Track
Registration & Breakfast
Future of Desktop Apps with JS (ElectronJs)
Nitin Pandit
Building Serverless Microservices Using Microsoft Azure
Vithal Wadje
Innovating RPA: A Robot for Every Person
Stephen Simon
Managing Cloud Storage Accounts using Logic Apps
Viknaraj Manogararajah
Data visualization using Python
Sekhar Srinivasan
Going Cross platform with AR Foundation
Vivek Sharma
Keynote
Managing your Azure dependencies in ASP.NET Core apps using VS
Bala Chirtsabesan
Securing Applications on Intelligent Azure
Abhishek Mishra
Getting started with Blazor the Framework of Future
S Ravi Kumar
Lunch
Build Progressive Web Apps using Angular 9
Debasis Saha
Build and deploy to any platform using Azure DevOps
Chervine Bhiwoo
Deep Dive in Azure Service Bus
Akshay Patel
Build a Native Mobile Application using React Native and JavaScript
Joseph Guadagno
Making sense of Web Job, Web Job SDK and Functions in Azure
Prakash Tripathi
CloudFront Distribution in AWS
Viral Jain
Tea Break
Introduction to PowerBI
Aakash Maurya
Build Advanced SPFx solutions with React and Graph API
Siddharth Vaghasia
Build Business Intelligence Analyst (BIA) Skills
Sundaram Subramanian
Deep dive of Power Platform – AI BUILDER
Prasham Sabadra
Panel 1
What's new in SharePoint development
Vipul Jain
Build a SSO (Single Sign On) based Native JavaScript application with Microsoft Identity within 10 minutes
Manoj Mittal
Panel 2
Applications and working of AI
Veena Sarda
Deploying serverless API's with .Net core 3.0 on AWS & Azure
Amey Vartak
Panel 3
Blockchain with .NET Core (Ark)
Anshu Kumari
Closing Note & Prize Distribution
Dev Track
Cloud Track
Architecture Track
Emerging Tech Track
Registration & Breakfast
Creating Full-Stack Web Apps Using Server-Side Blazor
Ankit Sharma
Real time face recognition with MS Cognitive Services
Niloshima Srivastava
Building Scalable APIs with GraphQL
Jeetendra Gund
Future of development with AI and Blockchain
Navdeep Garg
Debugging Tips and Tricks with Visual Studio 2019
Joseph Guadagno
Azure Containers
Abhishek Kant
Enterprise Architecture
Naveen Sharma
Bot Framework - learn it fast and look like a boss!
Allen O’Neill
Keynote
.Net Core & C# 8 Performance
David McCarter
Working with Azure kubernetes services
Ritesh Modi
Becoming an Architect
Vidyavrat Agarwal
Why Techies Need to Learn Product Management
Saurabh Jain
Lunch
Build a rules engine in .Net Core
Sanjay Vyas
Building CI and CD Pipeline using Azure DevOps
Sandeep Soni
Entity Framework Core - Tips and Tricks, Performance Optimization, and Tuning
Bassam Alugili
Hacking your way into Data Science
Sanket Verma
Speed up your .Net Core Website
Sourabh Somani
Azure
Magnus Mårtensson
Demystifying Open Distro for Elasticsearch
Suman Debnath
Future of Data
Shivam Ahuja
Tea Break
gRPC with C# and .Net Core
Mangesh Gaherwar
Panel 1
Essentials of Cloud security
Parveen Malik
Power platform and Dynamics 365
Deepesh Somani
Microservices - the gRPC Way
Viswanatha Swamy
Panel 2
Reserved
Reserved
Closing Note & Prize Distribution
Using Azure Load Balancer for High Availability of .NET Services
A reliable .NET application must continue serving users when a virtual machine fails, maintenance takes a node offline, or traffic increases suddenly. Azure Load Balancer provides a foundation for this resilience by distributing network traffic across healthy compute instances. When it is combined with well-designed ASP.NET Core services, availability zones, health monitoring, and automated scaling, it can remove individual servers as single points of failure.
Azure Load Balancer operates at Layer 4 of the network stack. It handles TCP and UDP connections without inspecting application content, which makes it efficient for high-volume traffic and suitable for many kinds of .NET workloads. It can expose a service through a public IP address or distribute traffic privately inside an Azure virtual network.
High availability, however, depends on more than placing several servers behind a frontend IP. The application must be stateless where possible, the load balancer must know when an instance is unhealthy, and deployment processes must allow connections to drain safely. These design decisions determine whether a .NET service recovers cleanly or simply moves failures from one component to another.
Where Azure Load Balancer Fits
Azure Load Balancer uses a frontend configuration, a backend pool, health probes, and load-balancing rules. The frontend provides the IP address clients use. The backend pool contains virtual machines or virtual machine scale set instances. A rule maps a frontend port and protocol to a backend port, while a health probe determines which instances are eligible to receive new traffic.
A public load balancer is appropriate when clients connect from the internet to an application hosted on Azure virtual machines or a scale set. An internal load balancer uses a private IP address and is useful for service-to-service communication, internal APIs, database tiers, or private applications. A common architecture uses both: public traffic reaches an edge tier, while internal .NET services communicate through private load-balancing endpoints.
Because the service works at the transport layer, it does not understand HTTP routes, cookies, authentication claims, or application responses. This simplicity is valuable for performance and protocol flexibility, but it also means that application-level routing belongs elsewhere. Azure Application Gateway or Azure Front Door may be a better choice when a solution needs web application firewall features, URL-based routing, TLS termination, or global traffic distribution.
Designing A Resilient .NET Backend
The backend pool should contain multiple independent instances rather than several processes on one virtual machine. A Virtual Machine Scale Set is often a practical choice because it supports consistent configuration, instance replacement, autoscaling, and integration with availability zones. Place instances across zones when the selected Azure region and workload support zonal deployment.
An ASP.NET Core service behind a load balancer should generally avoid storing request state in local memory. If a user’s session exists only on one server, a later request routed to another instance can lose that state. Store shared session data in a suitable distributed cache, database, or other durable service. Authentication should likewise use tokens or shared data-protection keys so every instance can validate requests consistently.
File uploads and generated documents require the same discipline. Local disk is temporary from the perspective of a scalable service. Use Azure Blob Storage or another shared storage service for durable files, and keep configuration in managed services such as Azure App Configuration or Key Vault where appropriate. This allows a replacement instance to start with the same operational context as its peers.
Connection management also affects resilience. Configure database connection pools carefully, apply retry policies only to transient failures, and use timeouts and cancellation tokens in outbound calls. A load balancer can redirect new connections, but it cannot make a blocked database call complete. The service itself must fail quickly and recover predictably.
Health Probes And Traffic Distribution
A health probe is the mechanism that prevents Azure Load Balancer from sending new flows to an unavailable instance. For a TCP probe, Azure checks whether a port accepts connections. An HTTP or HTTPS probe can request a path and interpret the response. For a .NET API, a dedicated health endpoint is usually more meaningful than checking only whether the web server process is listening.
A liveness endpoint can indicate that the process is running, while a readiness endpoint can verify that essential dependencies are available. These checks should be designed carefully. If readiness requires every optional downstream service to be online, a temporary dependency issue may remove every backend from rotation. Conversely, a probe that always returns success can keep a broken instance in service.
Probe settings should reflect the service’s startup and recovery behavior. A newly launched instance may need time for application initialization, database migrations, cache warming, or certificate loading. Configure the probe interval, unhealthy threshold, and probe path so Azure can detect genuine failures without causing unnecessary flapping.
Load Balancer distributes new flows according to its configured distribution mode. Existing connections are not automatically moved when a backend becomes unhealthy. This distinction matters for long-lived TCP connections, SignalR applications, and custom protocols. The client or an upstream component must reconnect after a connection is broken, and the application should support reconnection without duplicating operations.
| Capability | Azure Load Balancer | Application Gateway | Azure Front Door |
|---|---|---|---|
| Network layer | Layer 4 TCP and UDP | Layer 7 HTTP and HTTPS | Global Layer 7 HTTP and HTTPS |
| Typical scope | Regional virtual networks | Regional web applications | Global web entry point |
| Routing | IP, port, and protocol based | Host, path, cookie, and HTTP features | Global routing, host, path, and acceleration |
| TLS termination | Limited compared with Layer 7 services | Supported | Supported |
| Web application firewall | Not provided | Available | Available |
| Common .NET use | High-throughput services on VMs or VM Scale Sets | Regional ASP.NET web applications | Multi-region public applications and APIs |
Handling Failover And Deployments
High availability includes planned maintenance as well as unexpected failure. During a rolling deployment, instances should be updated in small batches while healthy capacity remains available. A new version should pass startup validation and health checks before the old instance is removed. This approach reduces the chance that a deployment takes the entire service offline.
Connection draining deserves special attention. Azure Load Balancer can support graceful shutdown patterns through the application and platform configuration, but the .NET service must cooperate. When an instance receives a termination signal, it should stop accepting new work, allow active requests a reasonable time to finish, and close resources cleanly. Long-running jobs should be placed on a durable queue rather than tied to the lifetime of an HTTP request.
Availability Zones protect against failures affecting a datacenter within a region, while multiple regions address larger regional disruptions. A regional load balancer alone does not provide multi-region failover. For that design, combine regional deployments with a global routing service, health-based DNS, or Azure Front Door, depending on routing, security, and latency requirements.
Disaster recovery should be tested rather than assumed. Simulate a failed instance, remove a backend from service, restart the application, and validate that clients experience acceptable behavior. Test dependency failures too, because a perfectly healthy load-balancing layer cannot compensate for an unavailable identity provider, database, queue, or storage account.
Observability And Security
Monitoring should cover both the load balancer and the .NET application. Useful signals include health probe status, data-path availability, frontend and backend traffic, failed connections, latency, HTTP status codes, request rates, CPU, memory, and dependency timings. Application Insights and Azure Monitor can correlate service-level failures with infrastructure events.
Logging should identify the instance that processed each request. Include a correlation identifier and avoid logging sensitive values such as access tokens or personal information. When traffic shifts after a failure, these details help engineers determine whether the problem originated in one backend, a shared dependency, or the network path.
Network security groups should permit only the traffic required by the architecture. Backend instances do not need to be broadly exposed when clients reach them through a public load balancer. Restrict administrative access, use private connectivity for internal services, and protect management ports through controlled access methods.
TLS remains an application and platform concern. A public load balancer can distribute encrypted TCP traffic, but certificate termination and HTTP-aware security may require Application Gateway, Front Door, or the .NET application itself. Select the termination point deliberately, then document how certificates are stored, renewed, and deployed without service interruption.
Practical Choices For A Production Service
The appropriate design depends on protocol, scope, and operational needs. A small regional ASP.NET Core API running on a pair of virtual machines may need only an internal or public load balancer, a proper readiness probe, shared configuration, and reliable monitoring. A high-volume public application may require a scale set across zones, automated deployment, distributed state, and a separate global entry layer.
Avoid treating the load balancer as an application recovery mechanism. It can stop directing new connections to an unhealthy backend, but it cannot repair bad code, restore deleted data, or coordinate business transactions. Reliability comes from the complete system: resilient services, durable dependencies, automation, observability, and tested recovery procedures.
A disciplined implementation usually follows these practices:
- Deploy at least two backend instances across failure domains where the workload and region support it.
- Create a dedicated readiness endpoint that checks essential service conditions without introducing unnecessary dependency coupling.
- Keep session state, files, configuration, and cryptographic keys available to every instance.
- Use rolling deployments, graceful shutdown, and idempotent operations for safe failover and upgrades.
- Monitor probe health, connection behavior, application telemetry, and dependency failures together.
Applying The Pattern To .NET Services
A useful reference architecture begins with clients connecting to a public frontend IP or an upstream global service. Azure Load Balancer sends eligible flows to a backend pool containing ASP.NET Core instances in a Virtual Machine Scale Set. Each instance exposes a health endpoint, uses shared state where necessary, and communicates with internal services over private network paths.
For internal microservices, an internal load balancer can provide a stable private endpoint while individual service instances scale behind it. This pattern avoids exposing every service publicly and simplifies client configuration. Service discovery, authentication, retries, and timeout policies still need to be addressed at the application or platform layer.
The design should also account for observability during failure. When one instance becomes unhealthy, operations teams need to see the probe transition, the resulting traffic change, and the user-facing effect. A short recovery time is valuable, but a clear explanation of what happened is essential for improving capacity planning and operational controls.
The C# Corner Annual Conference 2020 provides a useful setting for exploring these ideas alongside broader subjects such as Azure, cloud computing, DevOps, web development, data, and AI. Conference sessions and speaker perspectives can help connect infrastructure choices with the practices required to build, deploy, and operate modern .NET systems.
Explore the conference agenda, speaker profiles, and Azure-focused learning resources to deepen your understanding of resilient cloud architecture. Apply the load-balancing pattern in a test environment, measure its behavior during failures, and carry those findings into production design and deployment decisions.
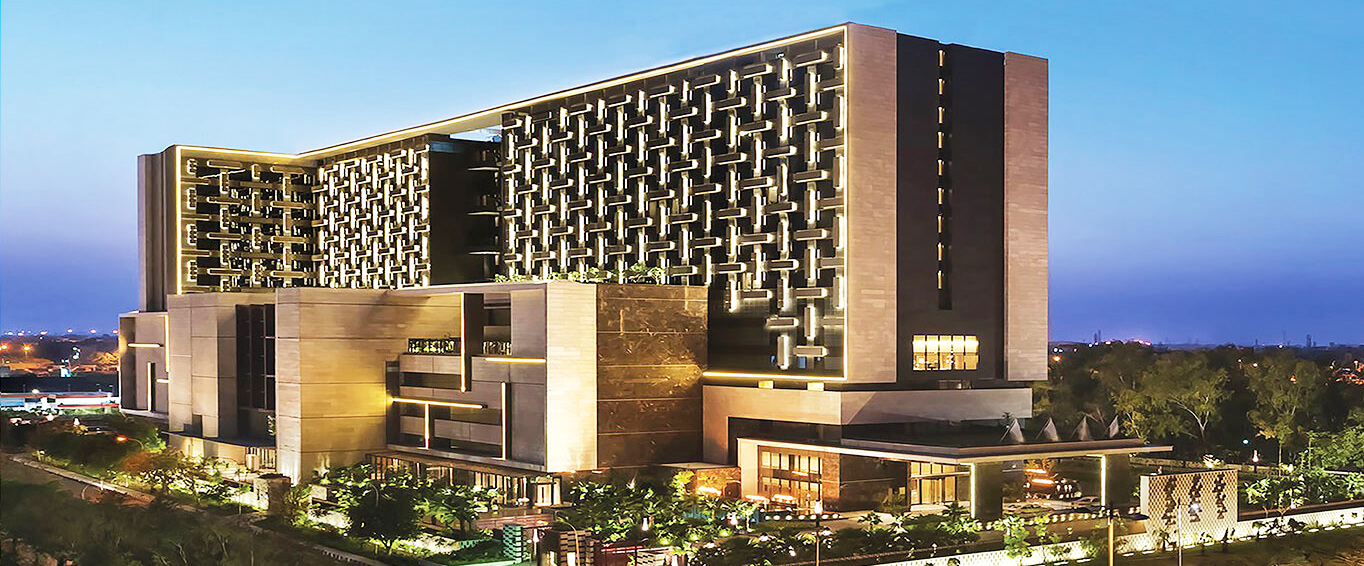
1, CBD, Maharaj Surajmal Road, Near Yamuna Sports Complex, Delhi, 110032
GENERAL QUERIES
Manish Tewatia
manish@csharpcon.com
+91-9718-431-042
TICKET QUERIES
Atul Gupta
conference@csharpcon.com
+91-9910-125-804