Presents
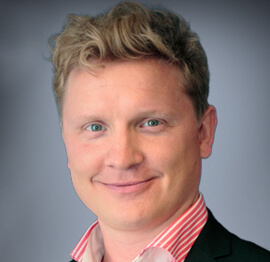
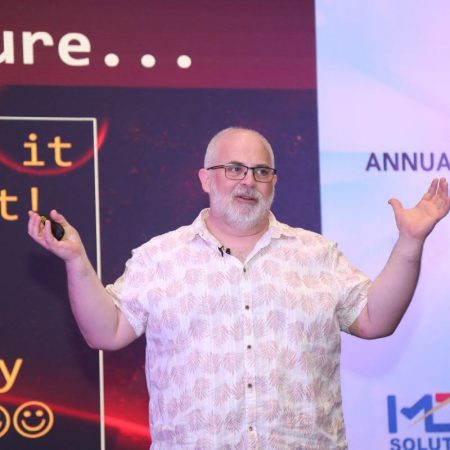
Magnus Mårtensson
Microsoft Regional Director, Azure MVP, CEO Loftysoft
Avirag Jain
Director & CTO R Systems
Mahesh Chand
Founder C# Corner, CEO Mindcracker
Chris Gali
CEO & Co-Founder Graphite
Subinder Khurana
Chief Architect StoryProcess, Founder NASSCOM DeepTech Club
Bryan Rishforth
Investor, Chairman Graphite
Bryn Everson
Director Biz Dev Graphite
Raj Tiwari
Digital Transformation Leader, Futurist and Visionary
Joseph Guadagno
Microsoft MVP, Lead Quicken Loans
Nikita Sachdev
Entrepreneur, Blockchain Enthusiast & Advisor, Social Media Influencer
Doug Wagner
COO & Founder Adapt Technical Group
Ritesh Modi
Architect, Senior Evangelist, Cloud Architect
Crystal Wenrick
Director Communications Mindcracker
Allen O’Neill
Microsoft MVP, Consulting Engineer/Architect
Praveen Kumar
CEO MCN Solutions
Chris Love
Founder Love2Dev, Microsoft MVP, Author
Sanjay Vyas
Microsoft Regional Director, Microsoft MVP, Founder & CEO SkillLabs Technologies
Veena Sarda
Deep Learning Consultant, Author
Sekhar Srinivasan
C# Corner MVP, Microsoft Certified Trainer, Pluralsight Author
Lalit Bansal
Founder & CEO - EIY SYS
Navdeep Garg
CEO Revinfotech
Prakash Tripathi
Tech Manager/Leader, Microsoft MVP, Blogger
Bhavna Jain
Breakthrough Consultant
Naveen Sharma
Enterprise Architect, Leadership Coach, Author
Vidya Vrat Agarwal
Principal Architect, Microsoft MVP, Author
Sheetal Agarwal
Founder Clownselors, Medical Clown, Trainer
Abhishek Kant
Founder GTM Catalyst
Vishnu Saran
Founder & CEO VoiceQube
Sandeep Soni
Founder & CEO Deccansoft, Microsoft Certified Trainer
Parveen Malik
AVP InfoSec & Vulnerability Management, Information Security Expert
Nitin Pandit
Microsoft MVP, Developer Evangelist, Author
Niloshima Srivastava
C# Corner MVP, Tech Architect, Trainer, Blogger
Bala Chirtsabesan
Senior Software Engineer at Microsoft, Author
Manoj Mittal
Sr. Technical Architect, C# Corner MVP, Author
Chandni Di
Co-Founder Voice of Slum
Vithal Wadje
Technical Lead, Microsoft MVP, Author
Shivam Ahuja
Founder SkillCircle, Business Mentor
Chervine Bhiwoo
Solution Architect, Microsoft MVP, Author
Saurabh Jain
Vice President Paytm, Founder Fun2Do Labs, Author
Vinay Solanki
Head IoT at Lenovo, Founder IoT-NCR
Anshu kumari
Founder Blockchainkids, Inventor, Trainer
Amit Singal
CEO Startup Buddy
Dev Pratap
Co-Founder & CEO Voice of Slum
Amey Vartak
Technology Consultant, Full Stack Developer, C# Corner MVP, Author
Viswanatha Swamy
Principal Software Engineer, C# Corner MVP, Author
Sanket Verma
Research Engineer @ Ballistics (Forensics) and Chair, PyData Delhi
Sourabh Somani
Lead Developer, Microsoft MVP, Author
Abhishek Mishra
Software Architect, C# Corner MVP, Author
Siddharth Vaghasia
Technical Consultant, C# Corner MVP, Blogger
Bassam Alugili
Senior Software Specialist, Database Expert
S Ravi Kumar
Solution Architect, C# Corner MVP, Author
Sundaram Subramanian
Full Stack Developer, C# Corner MVP, Speaker
Deepesh Somani
Solution Architect, Microsoft MVP, Author
Debasis Saha
Technical Project Manager, C# Corner MVP, Blogger, Author
Vipul Jain
Software Architect, C# Corner MVP, Author
Akshay Patel
Technical Architect, Microsoft Certified Trainer, C# Corner MVP, Author
Stephen Simon
RPA Developer, Evangelist, Author
Vivek Sharma
Founder Kingster636, AR/VR Specialist
Jeetendra Gund
Technical Lead, C# Corner MVP, Author
Sujal Beniwal
AI Enthusiast, Student
M Viknaraj
Microsoft MVP, Azure Architect, Author
Prasham Sabadra
Software Architect, C# Corner MVP, Trainer, Author
Aakash Maurya
Senior Developer, C# Corner MVP, Speaker
Ankit Sharma
Senior Software Engineer, C# Corner MVP, Author
Mangesh Gaherwar
Team Lead, C# Corner MVP, Author
Viral Jain
Technical Consultant, C# Corner MVP, Author
Bhasker Das
Solution Architect, Evangelist
Manish Dwivedi
Associate Project Manager
Ck Nitin
Programmer, Author
Rohit Gupta
Technical Trainer, Author
Manish Tewatia
Full-stack Marketer, UX Designer
Bhavya Gaur
Technical Illustrator
Rohit Tomar
SEO/SMO Expert
Web Track
Cloud & Data Track
Dev Track
Registration & Breakfast
Future of Desktop Apps with JS (ElectronJs)
Nitin Pandit
Building Serverless Microservices Using Microsoft Azure
Vithal Wadje
Innovating RPA: A Robot for Every Person
Stephen Simon
Managing Cloud Storage Accounts using Logic Apps
Viknaraj Manogararajah
Data visualization using Python
Sekhar Srinivasan
Going Cross platform with AR Foundation
Vivek Sharma
Keynote
Managing your Azure dependencies in ASP.NET Core apps using VS
Bala Chirtsabesan
Securing Applications on Intelligent Azure
Abhishek Mishra
Getting started with Blazor the Framework of Future
S Ravi Kumar
Lunch
Build Progressive Web Apps using Angular 9
Debasis Saha
Build and deploy to any platform using Azure DevOps
Chervine Bhiwoo
Deep Dive in Azure Service Bus
Akshay Patel
Build a Native Mobile Application using React Native and JavaScript
Joseph Guadagno
Making sense of Web Job, Web Job SDK and Functions in Azure
Prakash Tripathi
CloudFront Distribution in AWS
Viral Jain
Tea Break
Introduction to PowerBI
Aakash Maurya
Build Advanced SPFx solutions with React and Graph API
Siddharth Vaghasia
Build Business Intelligence Analyst (BIA) Skills
Sundaram Subramanian
Deep dive of Power Platform – AI BUILDER
Prasham Sabadra
Panel 1
What's new in SharePoint development
Vipul Jain
Build a SSO (Single Sign On) based Native JavaScript application with Microsoft Identity within 10 minutes
Manoj Mittal
Panel 2
Applications and working of AI
Veena Sarda
Deploying serverless API's with .Net core 3.0 on AWS & Azure
Amey Vartak
Panel 3
Blockchain with .NET Core (Ark)
Anshu Kumari
Closing Note & Prize Distribution
Dev Track
Cloud Track
Architecture Track
Emerging Tech Track
Registration & Breakfast
Creating Full-Stack Web Apps Using Server-Side Blazor
Ankit Sharma
Real time face recognition with MS Cognitive Services
Niloshima Srivastava
Building Scalable APIs with GraphQL
Jeetendra Gund
Future of development with AI and Blockchain
Navdeep Garg
Debugging Tips and Tricks with Visual Studio 2019
Joseph Guadagno
Azure Containers
Abhishek Kant
Enterprise Architecture
Naveen Sharma
Bot Framework - learn it fast and look like a boss!
Allen O’Neill
Keynote
.Net Core & C# 8 Performance
David McCarter
Working with Azure kubernetes services
Ritesh Modi
Becoming an Architect
Vidyavrat Agarwal
Why Techies Need to Learn Product Management
Saurabh Jain
Lunch
Build a rules engine in .Net Core
Sanjay Vyas
Building CI and CD Pipeline using Azure DevOps
Sandeep Soni
Entity Framework Core - Tips and Tricks, Performance Optimization, and Tuning
Bassam Alugili
Hacking your way into Data Science
Sanket Verma
Speed up your .Net Core Website
Sourabh Somani
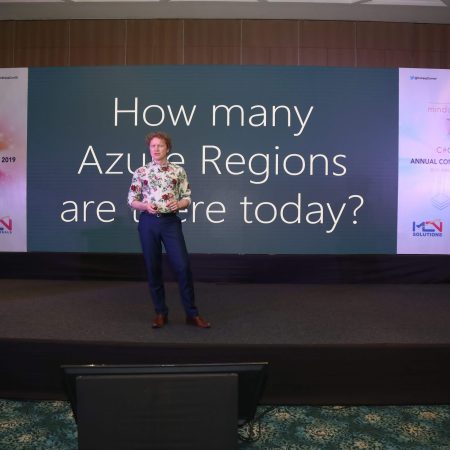
Azure
Magnus Mårtensson
Demystifying Open Distro for Elasticsearch
Suman Debnath
Future of Data
Shivam Ahuja
Tea Break
gRPC with C# and .Net Core
Mangesh Gaherwar
Panel 1
Essentials of Cloud security
Parveen Malik
Power platform and Dynamics 365
Deepesh Somani
Microservices - the gRPC Way
Viswanatha Swamy
Panel 2
Reserved
Reserved
Closing Note & Prize Distribution
Keeping Connection Strings Safe in .NET Apps with Azure Key Vault
Most .NET developers reach for the web.config or appsettings.json file the moment they need to point a SqlConnection somewhere, and honestly, that habit is hard to shake. It works, it is familiar, and it survives a redeploy without complaint. The trouble starts the moment the file leaves your laptop. Connection strings, SAS tokens and API keys get pasted into source control, dropped into chat windows, or copied into deployment pipelines that nobody reviews properly. In a small team this might feel harmless, but it is exactly the kind of slow leak that auditors flag and attackers love.
Azure Key Vault offers a cleaner home for these strings. Instead of scattering secrets across every environment file, you store them once in a vault, control access with policies and identities, and let your .NET application fetch what it needs at runtime. For teams working from Sydney, Melbourne or a Brisbane office, this also aligns nicely with Australian data sovereignty expectations and the local regulatory landscape, which we will get to shortly.
There is a fair dinkum shift happening in how we treat configuration. The old model treated secrets as code; the new model treats them as data that lives outside the binary. Once you make that mental switch, the tooling around Azure Key Vault stops looking like overkill and starts looking like the obvious choice. If you want to see how this approach is being discussed by Australian developers in person, the C# Corner Conference is a good place to start.
Why connection strings deserve better than appsettings.json
The appsettings.json file is brilliant for non-sensitive configuration. Logging levels, feature flags, pagination defaults — all fair game. Connection strings are a different beast. They often contain usernames, sometimes inline passwords, and frequently grant far more access than the calling code actually needs. Putting a production database credential into a file that gets bundled into a container image means anyone with read access to that image can read the credential.
Beyond the accidental leak, there is a versioning problem. Every change to a connection string becomes a code change, which means a pull request, a code review, and a deployment. That is fine when you tweak a development setting once a quarter, but it slows you down when security asks you to rotate a database password tomorrow morning. Keeping the string in Key Vault separates the cadence of code changes from the cadence of credential changes, and that separation is where the real productivity gain lives.
A quick comparison helps frame the trade-offs. Here is how the two approaches stack up for typical .NET scenarios.
| Concern | appsettings.json | Azure Key Vault |
|---|---|---|
| Secret rotation | Requires redeploy | Updated centrally, no redeploy |
| Access auditing | Limited to source control logs | Full activity log per secret |
| Access control | Whoever can read the file | RBAC, access policies, managed identity |
| Risk of accidental commit | High | Low, secrets never touch the repo |
| Local development | Plain text on disk | Use SecretManager tool or user-assigned identity |
| Compliance posture | Often flagged in audits | Easier to align with APRA CPS 234 |
The last row matters more in Australia than in many other markets. The Australian Prudential Regulation Authority's CPS 234 standard expects financial organisations to keep tight control over information assets, and storing production database strings in a JSON file checked into Git is a finding waiting to happen.
Spinning up a vault in an Australian region
Before your application can read anything, you need a vault. The portal makes this painless, but a few choices deserve a thought. Region selection is the first. If your application and database live in Australia East or Australia Southeast, put the vault in the same region. Latency stays low, and you sidestep cross-border data movement questions that legal teams love to ask. Azure exposes both regions, with Australia Southeast in Victoria sometimes preferred by organisations in Melbourne because of the proximity and the way peering works with on-premises integrations.
Next, decide between access policies and Azure RBAC. For smaller teams, access policies are quicker to configure and easier to reason about. For larger enterprises that already standardise on RBAC across subscriptions, role-based authorisation gives a familiar model and integrates with Privileged Identity Management. Either approach works; mixing them in a single vault leads to confusion, so pick one and stick with it.
Soft delete and purge protection are non-negotiable in a regulated environment. Turn both on during creation rather than after, because enabling purge protection later requires a fresh vault. With those settings in place, even an accidental deletion by a well-meaning developer on a Friday arvo will not take your secrets with it.
Authenticating without storing credentials
The classic chicken-and-egg problem with Key Vault is this: your app needs a credential to read the credential store. The fix is managed identity, and it is the single biggest reason developers stop rolling their own solutions. When you enable a system-assigned managed identity on an App Service, Function App or VM, Azure creates a service principal behind the scenes and rotates its secret automatically. Your code simply calls DefaultAzureCredential and lets the Azure SDK work out which identity to use.
In a local development environment, DefaultAzureCredential falls back to your Azure CLI login, which is convenient when you are bouncing between cafes in Surry Hills and the office. In CI pipelines, swap in a workload identity federation so that your build agent never needs a long-lived client secret. The point is that the application code stays identical across environments, while the identity mechanism changes underneath.
If your application runs on something that does not yet support managed identities, such as an older on-premises server, fall back to a service principal with a certificate rather than a secret. Certificates are easier to rotate and harder to leak in a build log, and they fit comfortably inside an Azure DevOps library or a GitHub Actions secret. Whatever you do, avoid putting a client secret back into appsettings.json; you have just moved the problem rather than solved it.
Reading secrets at startup and refreshing them safely
The simplest pattern is to read all required secrets during application startup and cache them in memory. ASP.NET Core's AddAzureKeyVault extension wires this up with a few lines in Program.cs, and the IConfiguration provider transparently exposes each secret as a configuration value. For a connection string, you might retrieve it with Configuration.GetConnectionString("PrimaryDb") and pass it straight into your DbContext options.
Caching has trade-offs. A cached secret means your app does not make a network call on every database query, which is good for performance and good for hitting the Key Vault throttling limits. The downside is that a rotation does not take effect until the next restart. For most line-of-business applications this is acceptable, but for systems handling payments or patient records, you may want a shorter refresh window.
A more advanced pattern uses IConfigurationRoot.Reload() on a timer, or wires up Azure Key Vault's event grid notifications to invalidate a cache when a secret changes. This is a small amount of extra code but a big operational win, especially when the security team in your Sydney CBD office insists on monthly rotation without any downtime.
Rotating secrets without redeploying
Rotation is the moment of truth for any secret management strategy. With Key Vault, the workflow is straightforward. Update the secret value in the portal or through the CLI, optionally set an activation date if you are using staged rotation, and let consumers pick up the new value on their next read. No application redeploy, no config push, no emergency change window.
For database credentials, consider pairing Key Vault with Azure SQL's own automatic rotation features where supported. The pattern is usually a dual-credential model: the application presents both the old and the new password during a transition window, and the database accepts either. Once the transition window closes, you remove the old credential from Key Vault entirely.
Australian organisations under APRA oversight often tie rotation cadences to documented control testing. Having the rotation runbook living alongside the vault, with audit logs in Log Analytics, makes the next CPS 234 assessment noticeably less painful. It is also a good conversation starter when comparing notes with peers at local .NET user groups in Melbourne or Brisbane.
Compliance habits and the Australian context
A vault is only as trustworthy as the habits around it. Treat secret values as write-only from a developer perspective. If someone on your team needs to read a production connection string, that is a smell; build a deployment pipeline that injects the secret directly into the application instead. Audit the access policies quarterly, and prune any service principal that no longer needs access.
Australian privacy law adds a few wrinkles. The Privacy Act and the Australian Privacy Principles expect organisations to protect personal information, and connection strings that grant access to a customer database sit squarely in scope. Hosting your vault in an Australian region, keeping the activity log in Australia, and restricting access via Conditional Access policies are all practical steps that map cleanly to those obligations.
Finally, do not forget the boring parts. Backups, disaster recovery drills, and a documented runbook for what to do if the vault becomes unavailable. A cached fallback configuration, even a stripped-down one, can keep a checkout flow alive while the platform team investigates. Pair that with sensible alerts on vault health in Application Insights, and you have a setup that survives both a bad Tuesday morning and a regulator's questionnaire on a quiet Friday arvo.
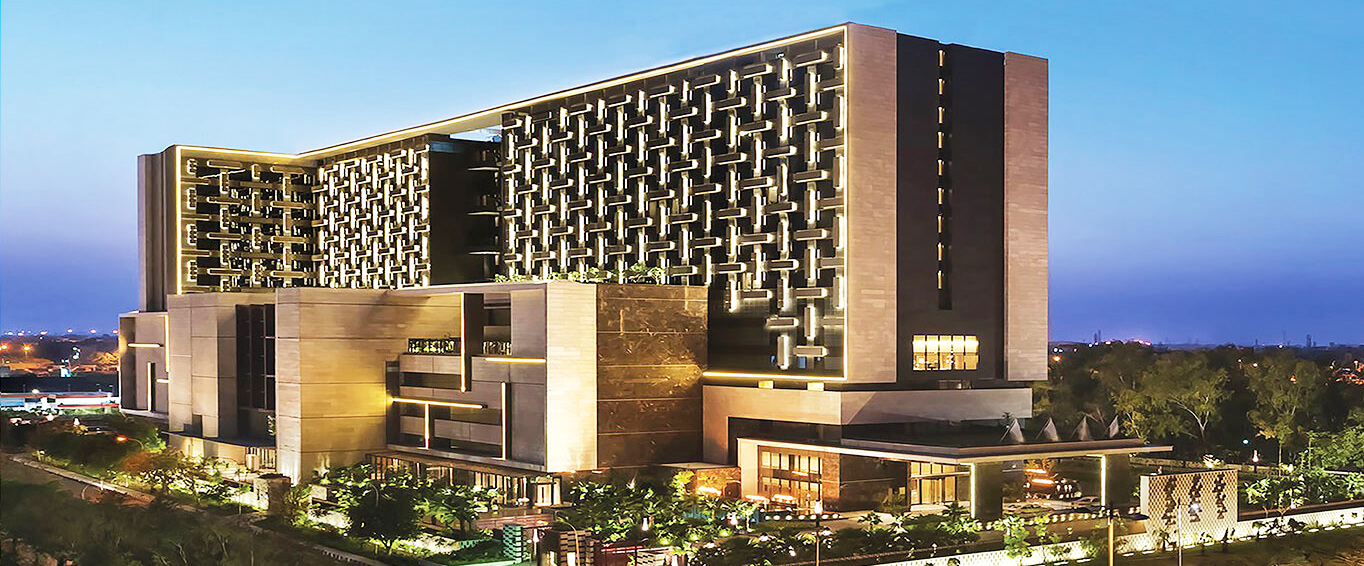
1, CBD, Maharaj Surajmal Road, Near Yamuna Sports Complex, Delhi, 110032
GENERAL QUERIES
Manish Tewatia
manish@csharpcon.com
+91-9718-431-042
TICKET QUERIES
Atul Gupta
conference@csharpcon.com
+91-9910-125-804