Presents
Magnus Mårtensson
Microsoft Regional Director, Azure MVP, CEO Loftysoft
Avirag Jain
Director & CTO R Systems
Mahesh Chand
Founder C# Corner, CEO Mindcracker
Chris Gali
CEO & Co-Founder Graphite
Subinder Khurana
Chief Architect StoryProcess, Founder NASSCOM DeepTech Club
Bryan Rishforth
Investor, Chairman Graphite
Bryn Everson
Director Biz Dev Graphite
Raj Tiwari
Digital Transformation Leader, Futurist and Visionary
Joseph Guadagno
Microsoft MVP, Lead Quicken Loans
Nikita Sachdev
Entrepreneur, Blockchain Enthusiast & Advisor, Social Media Influencer
Doug Wagner
COO & Founder Adapt Technical Group
Ritesh Modi
Architect, Senior Evangelist, Cloud Architect
Crystal Wenrick
Director Communications Mindcracker
Allen O’Neill
Microsoft MVP, Consulting Engineer/Architect
Praveen Kumar
CEO MCN Solutions
Chris Love
Founder Love2Dev, Microsoft MVP, Author
Sanjay Vyas
Microsoft Regional Director, Microsoft MVP, Founder & CEO SkillLabs Technologies
Veena Sarda
Deep Learning Consultant, Author
Sekhar Srinivasan
C# Corner MVP, Microsoft Certified Trainer, Pluralsight Author
Lalit Bansal
Founder & CEO - EIY SYS
Navdeep Garg
CEO Revinfotech
Prakash Tripathi
Tech Manager/Leader, Microsoft MVP, Blogger
Bhavna Jain
Breakthrough Consultant
Naveen Sharma
Enterprise Architect, Leadership Coach, Author
Vidya Vrat Agarwal
Principal Architect, Microsoft MVP, Author
Sheetal Agarwal
Founder Clownselors, Medical Clown, Trainer
Abhishek Kant
Founder GTM Catalyst
Vishnu Saran
Founder & CEO VoiceQube
Sandeep Soni
Founder & CEO Deccansoft, Microsoft Certified Trainer
Parveen Malik
AVP InfoSec & Vulnerability Management, Information Security Expert
Nitin Pandit
Microsoft MVP, Developer Evangelist, Author
Niloshima Srivastava
C# Corner MVP, Tech Architect, Trainer, Blogger
Bala Chirtsabesan
Senior Software Engineer at Microsoft, Author
Manoj Mittal
Sr. Technical Architect, C# Corner MVP, Author
Chandni Di
Co-Founder Voice of Slum
Vithal Wadje
Technical Lead, Microsoft MVP, Author
Shivam Ahuja
Founder SkillCircle, Business Mentor
Chervine Bhiwoo
Solution Architect, Microsoft MVP, Author
Saurabh Jain
Vice President Paytm, Founder Fun2Do Labs, Author
Vinay Solanki
Head IoT at Lenovo, Founder IoT-NCR
Anshu kumari
Founder Blockchainkids, Inventor, Trainer
Amit Singal
CEO Startup Buddy
Dev Pratap
Co-Founder & CEO Voice of Slum
Amey Vartak
Technology Consultant, Full Stack Developer, C# Corner MVP, Author
Viswanatha Swamy
Principal Software Engineer, C# Corner MVP, Author
Sanket Verma
Research Engineer @ Ballistics (Forensics) and Chair, PyData Delhi
Sourabh Somani
Lead Developer, Microsoft MVP, Author
Abhishek Mishra
Software Architect, C# Corner MVP, Author
Siddharth Vaghasia
Technical Consultant, C# Corner MVP, Blogger
Bassam Alugili
Senior Software Specialist, Database Expert
S Ravi Kumar
Solution Architect, C# Corner MVP, Author
Sundaram Subramanian
Full Stack Developer, C# Corner MVP, Speaker
Deepesh Somani
Solution Architect, Microsoft MVP, Author
Debasis Saha
Technical Project Manager, C# Corner MVP, Blogger, Author
Vipul Jain
Software Architect, C# Corner MVP, Author
Akshay Patel
Technical Architect, Microsoft Certified Trainer, C# Corner MVP, Author
Stephen Simon
RPA Developer, Evangelist, Author
Vivek Sharma
Founder Kingster636, AR/VR Specialist
Jeetendra Gund
Technical Lead, C# Corner MVP, Author
Sujal Beniwal
AI Enthusiast, Student
M Viknaraj
Microsoft MVP, Azure Architect, Author
Prasham Sabadra
Software Architect, C# Corner MVP, Trainer, Author
Aakash Maurya
Senior Developer, C# Corner MVP, Speaker
Ankit Sharma
Senior Software Engineer, C# Corner MVP, Author
Mangesh Gaherwar
Team Lead, C# Corner MVP, Author
Viral Jain
Technical Consultant, C# Corner MVP, Author
Bhasker Das
Solution Architect, Evangelist
Manish Dwivedi
Associate Project Manager
Ck Nitin
Programmer, Author
Rohit Gupta
Technical Trainer, Author
Manish Tewatia
Full-stack Marketer, UX Designer
Bhavya Gaur
Technical Illustrator
Rohit Tomar
SEO/SMO Expert
Web Track
Cloud & Data Track
Dev Track
Registration & Breakfast
Future of Desktop Apps with JS (ElectronJs)
Nitin Pandit
Building Serverless Microservices Using Microsoft Azure
Vithal Wadje
Innovating RPA: A Robot for Every Person
Stephen Simon
Managing Cloud Storage Accounts using Logic Apps
Viknaraj Manogararajah
Data visualization using Python
Sekhar Srinivasan
Going Cross platform with AR Foundation
Vivek Sharma
Keynote
Managing your Azure dependencies in ASP.NET Core apps using VS
Bala Chirtsabesan
Securing Applications on Intelligent Azure
Abhishek Mishra
Getting started with Blazor the Framework of Future
S Ravi Kumar
Lunch
Build Progressive Web Apps using Angular 9
Debasis Saha
Build and deploy to any platform using Azure DevOps
Chervine Bhiwoo
Deep Dive in Azure Service Bus
Akshay Patel
Build a Native Mobile Application using React Native and JavaScript
Joseph Guadagno
Making sense of Web Job, Web Job SDK and Functions in Azure
Prakash Tripathi
CloudFront Distribution in AWS
Viral Jain
Tea Break
Introduction to PowerBI
Aakash Maurya
Build Advanced SPFx solutions with React and Graph API
Siddharth Vaghasia
Build Business Intelligence Analyst (BIA) Skills
Sundaram Subramanian
Deep dive of Power Platform – AI BUILDER
Prasham Sabadra
Panel 1
What's new in SharePoint development
Vipul Jain
Build a SSO (Single Sign On) based Native JavaScript application with Microsoft Identity within 10 minutes
Manoj Mittal
Panel 2
Applications and working of AI
Veena Sarda
Deploying serverless API's with .Net core 3.0 on AWS & Azure
Amey Vartak
Panel 3
Blockchain with .NET Core (Ark)
Anshu Kumari
Closing Note & Prize Distribution
Dev Track
Cloud Track
Architecture Track
Emerging Tech Track
Registration & Breakfast
Creating Full-Stack Web Apps Using Server-Side Blazor
Ankit Sharma
Real time face recognition with MS Cognitive Services
Niloshima Srivastava
Building Scalable APIs with GraphQL
Jeetendra Gund
Future of development with AI and Blockchain
Navdeep Garg
Debugging Tips and Tricks with Visual Studio 2019
Joseph Guadagno
Azure Containers
Abhishek Kant
Enterprise Architecture
Naveen Sharma
Bot Framework - learn it fast and look like a boss!
Allen O’Neill
Keynote
.Net Core & C# 8 Performance
David McCarter
Working with Azure kubernetes services
Ritesh Modi
Becoming an Architect
Vidyavrat Agarwal
Why Techies Need to Learn Product Management
Saurabh Jain
Lunch
Build a rules engine in .Net Core
Sanjay Vyas
Building CI and CD Pipeline using Azure DevOps
Sandeep Soni
Entity Framework Core - Tips and Tricks, Performance Optimization, and Tuning
Bassam Alugili
Hacking your way into Data Science
Sanket Verma
Speed up your .Net Core Website
Sourabh Somani
Azure
Magnus Mårtensson
Demystifying Open Distro for Elasticsearch
Suman Debnath
Future of Data
Shivam Ahuja
Tea Break
gRPC with C# and .Net Core
Mangesh Gaherwar
Panel 1
Essentials of Cloud security
Parveen Malik
Power platform and Dynamics 365
Deepesh Somani
Microservices - the gRPC Way
Viswanatha Swamy
Panel 2
Reserved
Reserved
Closing Note & Prize Distribution
Securing SSL Certificates with Azure Key Vault in .NET
Transport Layer Security sits at the heart of every web application, yet managing the certificates that underpin it often becomes an afterthought. Developers tend to store .pfx files on disk, copy them between environments and rely on tribal knowledge to keep them renewed. In Australia, where organisations across Sydney, Melbourne and Brisbane must comply with the Privacy Act 1988 and the Notifiable Data Breaches scheme, that informal approach quickly becomes a liability. Moving certificate material into Azure Key Vault gives teams a hardened, auditable home for private keys while letting .NET applications fetch credentials on demand without ever persisting them locally.
The shift to cloud-based certificate management also dovetails with broader infrastructure modernisation. Many local enterprises are running workloads across the Australia East and Australia Southeast regions, where latency to end users is measured in single-digit milliseconds. By combining Key Vault with App Service, Azure Front Door or API Management, Australian teams can build regionally resilient endpoints whose TLS material is centrally governed, automatically rotated and tightly scoped through role-based access control. The remainder of this article walks through the practical steps of wiring Key Vault into a typical .NET stack, from initial provisioning through to renewal automation and local debugging.
Why Centralised Certificate Storage Matters
Certificate sprawl is one of the most common sources of unplanned downtime. A retail platform with stores across Perth, Adelaide and Canberra might run dozens of microservices, each requiring its own TLS credential. When expiry dates drift apart, an engineer eventually forgets one, browsers flag the site as untrusted and the on-call rotation spends a Saturday night issuing replacements under pressure. Centralised storage eliminates that pattern by giving every service a single source of truth and a single expiry calendar.
Beyond reliability, there are compliance motivations. The Australian Signals Directorate's Essential Eight maturity model calls for controlled access to authentication material, while APRA's CPS 234 standard requires banks and insurers to maintain an inventory of information assets with enforceable security controls. A Key Vault instance, backed by managed hardware security modules, satisfies both requirements because every read and write generates a log entry that can be shipped to Azure Monitor or a SIEM in Sydney. Auditors gain a complete record of who accessed which certificate and when, which is far stronger evidence than a screenshot of a shared network share.
There is also a developer experience benefit. Instead of passing .pfx blobs through build pipelines and storing them in obscure environment variables, a .NET application can request the certificate at startup. The private key never leaves the vault, the application identity is validated through Microsoft Entra ID, and the configuration story becomes consistent across development, staging and production. That consistency pays dividends when onboarding new engineers or migrating workloads to a new region.
Configuring Azure Key Vault for Certificate Storage
The first step is provisioning a vault, which can be done through the portal, Azure CLI or Bicep. For an Australian workload, choosing the Australia East region keeps data residency within the country, though Australia Central and Australia Southeast are also valid options depending on availability zone coverage. Soft delete should be enabled from day one to protect against accidental deletion, and purge protection added once the team is comfortable with the retention policy.
Certificates can be imported from an existing .pfx file or generated directly inside Key Vault. Generating inside the vault is preferable because the private key never traverses the developer's workstation. A typical CLI sequence might look like az keyvault certificate create --policy vault-ic-2024, where the policy defines the issuer (for example, DigiCert or Let's Encrypt), the key type, the validity period and the subject alternative names. The resulting certificate object exposes a kid identifier that .NET code uses for retrieval.
Access policies then bind specific Entra ID principals to certificate operations. A common pattern is to grant the application's managed identity get and list on certificates, while reserving create, import and delete for a privileged break-glass group. Network rules can further restrict the vault to private endpoints only, particularly relevant for financial services organisations subject to APRA oversight. With the vault hardened by Key Vault and policies in place, the certificate is ready to be consumed by code.
Integrating Key Vault with ASP.NET Core Applications
In an ASP.NET Core project, the Azure.Security.KeyVault.Certificates and Azure.Identity packages provide a clean abstraction layer. A managed identity is assigned to the App Service or container instance, removing the need for connection strings or client secrets. During application startup, the code uses CertificateClient with a DefaultAzureCredential instance, which automatically discovers the identity from the environment.
Retrieving a certificate is a matter of calling DownloadCertificateAsync with the certificate name. The returned X509Certificate2 object can be bound directly to Kestrel through the ListenOptions.UseHttps overload that accepts a callback. This approach keeps the private key material inside the Key Vault HSM boundary as long as the SDK version supports hardware-backed key export, which recent releases do through the KeyVaultKey API. For older .NET frameworks, a fallback path is to download the certificate into memory at startup and let Kestrel cache it.
Configuration can be sourced from Key Vault as well, using the AddAzureKeyVault extension on IConfigurationBuilder. Storing non-sensitive configuration alongside secrets reduces the number of endpoints the application must reach during cold start. When deploying to multiple regions, the VaultUri can be parameterised so that the same image runs in Sydney, Melbourne and offshore test environments without code changes.
Automating Certificate Renewal and Rotation
Manual renewal is the silent killer of certificate programmes. Key Vault mitigates this by supporting certificate authorities that participate in the auto-renewal flow, including DigiCert, GlobalSign and Let's Encrypt. Once the policy is configured with a lifetime action of daysBeforeExpiry, the vault will automatically request a new certificate before the old one expires and store both versions side by side.
Applications must still pick up the rotated material. Two patterns are common in .NET codebases. The first is a polling approach, where a background IHostedService refreshes the X509Certificate2 cache every few hours and rebinds Kestrel through a hot-swap mechanism. The second, more elegant pattern, uses Azure Event Grid to subscribe to Microsoft.KeyVault.CertificateNearExpiry events and trigger a redeploy or a configuration refresh. The latter integrates well with GitHub Actions runners hosted in Australian data centres, ensuring renewals happen during business hours rather than at 3 a.m. AEST.
Logging is essential to demonstrate control. Every successful renewal should produce a structured log entry tagged with the certificate name, the issuer and the new expiry. That log can be shipped to Log Analytics, where a Kusto query such as KeyVaultCertificateEvents | where OperationName == "Renew" provides an auditable trail. For organisations that need richer reporting, Power BI dashboards on top of Log Analytics have become a familiar sight in Melbourne-based operations centres.
Handling Local Development and Debugging
Developers working from home in Hobart or a co-working space in Parramatta cannot rely on managed identities when running code locally. The DefaultAzureCredential chain gracefully falls back to Visual Studio credentials, Azure CLI login or environment variables, but it can behave unpredictably when several identities are cached. The cleanest approach is to assign a dedicated developer Entra ID with tightly scoped access policies on a non-production vault and to share certificate names rather than values.
Another common pitfall is the well-known IP reminder that pops up the first time a public IP tries to authenticate against Azure services. While this is a security feature, it interrupts flow. Adding the developer's static IP to the vault's network rules, or running a small ExpressRoute or VPN tunnel into an Australian peering point, removes the friction. Local debug certificates can also be issued by a development CA installed on the machine, allowing Kestrel to serve HTTPS without ever touching the vault during unit tests.
Testing deserves its own vault instance. A separate Key Vault in the same resource group, populated with synthetic certificates, lets integration tests run end-to-end without risking production material. xUnit collections can share a single CertificateClient across tests to keep startup time under a second, and Testcontainers can spin up a vault emulator if the team wants fully offline runs. Treat the test vault with the same access discipline as production and you will avoid the familiar problem of test certificates leaking into staging.
Compliance, Auditing and Performance Considerations
From a regulatory standpoint, the Privacy Act and the Notifiable Data Breaches scheme treat cryptographic keys as personal information when they can be linked to an individual. Storing certificates in a vault with strict access policies, diagnostic logging and customer-managed keys provides defensible evidence that the organisation has implemented "reasonable steps" to protect that information. Combined with the Essential Eight's application control and patch management pillars, a Key Vault-centric design slots neatly into a broader security programme.
Performance is rarely a constraint, but worth measuring. A cold-start handshake against Key Vault adds roughly 100 to 200 milliseconds when the application boots in the same Azure region, and slightly more across regions. Caching the certificate in memory after the first fetch collapses that overhead for subsequent requests. For latency-sensitive APIs serving users in Sydney and Auckland, co-locating the vault with the compute resource and using premium SKU certificates backed by HSMs strikes the right balance between cost and throughput.
Finally, it pays to remember that certificate management rarely exists in isolation. The same Entra ID identities and managed identities that authenticate to Key Vault can authenticate to Service Bus, Storage and Cosmos DB. Architects building event-driven pipelines across multiple Australian regions often standardise on Key Vault as the credential plane, then layer messaging, queuing and storage on top. A practical walkthrough of that pattern can be found in the write-up on Using Azure Service Bus for Message Queuing in Distributed Systems, which complements the certificate-focused approach described here.
Practical Habits for Australian Teams
- Schedule certificate renewals during AEST business hours so on-call engineers can respond if the auto-renewal flow fails.
- Mirror production vaults between Australia East and Australia Southeast to survive a regional outage without manual failover.
- Rotate the break-glass access policy quarterly and store the recovery credentials in a physical safe rather than a password manager.
- Tag every certificate with the owning service, cost centre and environment so chargeback reports align with the FinOps practice common in larger enterprises.
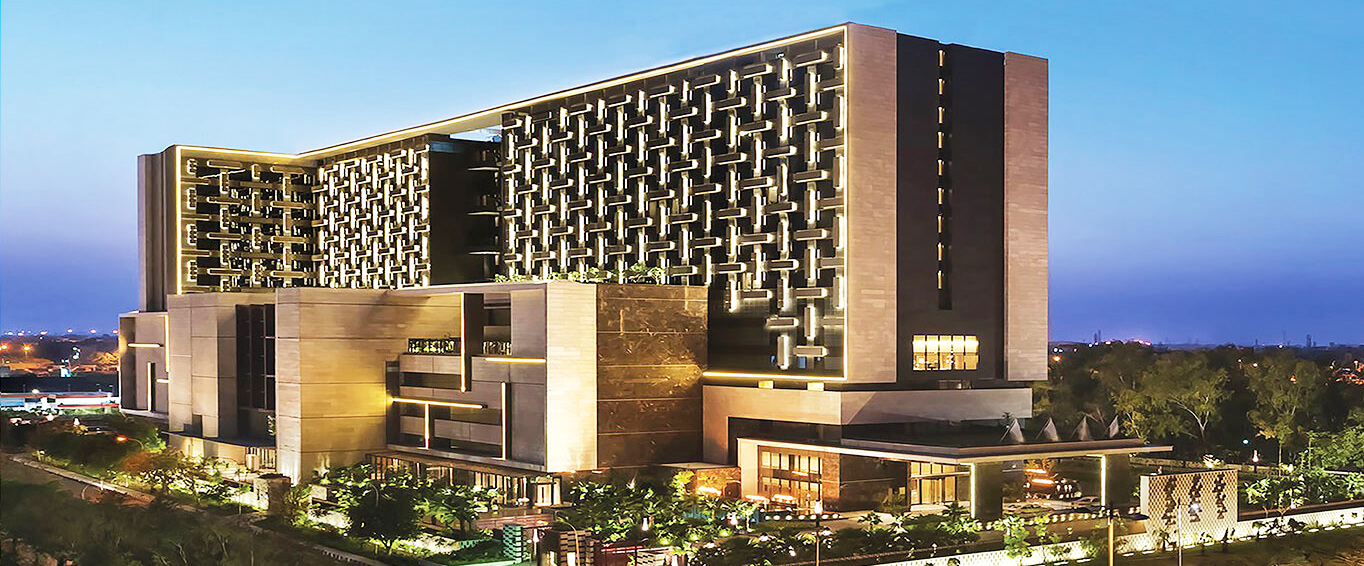
1, CBD, Maharaj Surajmal Road, Near Yamuna Sports Complex, Delhi, 110032
GENERAL QUERIES
Manish Tewatia
manish@csharpcon.com
+91-9718-431-042
TICKET QUERIES
Atul Gupta
conference@csharpcon.com
+91-9910-125-804