Presents
Magnus Mårtensson
Microsoft Regional Director, Azure MVP, CEO Loftysoft
Avirag Jain
Director & CTO R Systems
Mahesh Chand
Founder C# Corner, CEO Mindcracker
Chris Gali
CEO & Co-Founder Graphite
Subinder Khurana
Chief Architect StoryProcess, Founder NASSCOM DeepTech Club
Bryan Rishforth
Investor, Chairman Graphite
Bryn Everson
Director Biz Dev Graphite
Raj Tiwari
Digital Transformation Leader, Futurist and Visionary
Joseph Guadagno
Microsoft MVP, Lead Quicken Loans
Nikita Sachdev
Entrepreneur, Blockchain Enthusiast & Advisor, Social Media Influencer
Doug Wagner
COO & Founder Adapt Technical Group
Ritesh Modi
Architect, Senior Evangelist, Cloud Architect
Crystal Wenrick
Director Communications Mindcracker
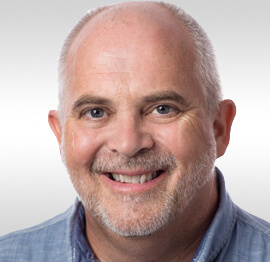
Allen O’Neill
Microsoft MVP, Consulting Engineer/Architect
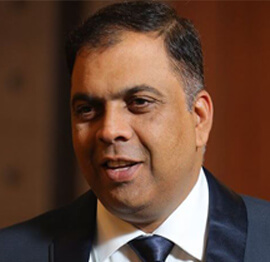
Praveen Kumar
CEO MCN Solutions
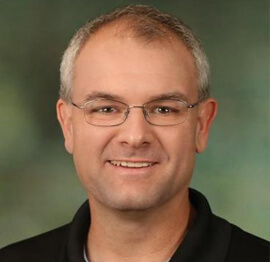
Chris Love
Founder Love2Dev, Microsoft MVP, Author
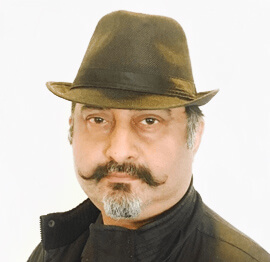
Sanjay Vyas
Microsoft Regional Director, Microsoft MVP, Founder & CEO SkillLabs Technologies
Veena Sarda
Deep Learning Consultant, Author
Sekhar Srinivasan
C# Corner MVP, Microsoft Certified Trainer, Pluralsight Author
Lalit Bansal
Founder & CEO - EIY SYS
Navdeep Garg
CEO Revinfotech
Prakash Tripathi
Tech Manager/Leader, Microsoft MVP, Blogger
Bhavna Jain
Breakthrough Consultant
Naveen Sharma
Enterprise Architect, Leadership Coach, Author
Vidya Vrat Agarwal
Principal Architect, Microsoft MVP, Author
Sheetal Agarwal
Founder Clownselors, Medical Clown, Trainer
Abhishek Kant
Founder GTM Catalyst
Vishnu Saran
Founder & CEO VoiceQube
Sandeep Soni
Founder & CEO Deccansoft, Microsoft Certified Trainer
Parveen Malik
AVP InfoSec & Vulnerability Management, Information Security Expert
Nitin Pandit
Microsoft MVP, Developer Evangelist, Author
Niloshima Srivastava
C# Corner MVP, Tech Architect, Trainer, Blogger
Bala Chirtsabesan
Senior Software Engineer at Microsoft, Author
Manoj Mittal
Sr. Technical Architect, C# Corner MVP, Author
Chandni Di
Co-Founder Voice of Slum
Vithal Wadje
Technical Lead, Microsoft MVP, Author
Shivam Ahuja
Founder SkillCircle, Business Mentor
Chervine Bhiwoo
Solution Architect, Microsoft MVP, Author
Saurabh Jain
Vice President Paytm, Founder Fun2Do Labs, Author
Vinay Solanki
Head IoT at Lenovo, Founder IoT-NCR
Anshu kumari
Founder Blockchainkids, Inventor, Trainer
Amit Singal
CEO Startup Buddy
Dev Pratap
Co-Founder & CEO Voice of Slum
Amey Vartak
Technology Consultant, Full Stack Developer, C# Corner MVP, Author
Viswanatha Swamy
Principal Software Engineer, C# Corner MVP, Author
Sanket Verma
Research Engineer @ Ballistics (Forensics) and Chair, PyData Delhi
Sourabh Somani
Lead Developer, Microsoft MVP, Author
Abhishek Mishra
Software Architect, C# Corner MVP, Author
Siddharth Vaghasia
Technical Consultant, C# Corner MVP, Blogger
Bassam Alugili
Senior Software Specialist, Database Expert
S Ravi Kumar
Solution Architect, C# Corner MVP, Author
Sundaram Subramanian
Full Stack Developer, C# Corner MVP, Speaker
Deepesh Somani
Solution Architect, Microsoft MVP, Author
Debasis Saha
Technical Project Manager, C# Corner MVP, Blogger, Author
Vipul Jain
Software Architect, C# Corner MVP, Author
Akshay Patel
Technical Architect, Microsoft Certified Trainer, C# Corner MVP, Author
Stephen Simon
RPA Developer, Evangelist, Author
Vivek Sharma
Founder Kingster636, AR/VR Specialist
Jeetendra Gund
Technical Lead, C# Corner MVP, Author
Sujal Beniwal
AI Enthusiast, Student
M Viknaraj
Microsoft MVP, Azure Architect, Author
Prasham Sabadra
Software Architect, C# Corner MVP, Trainer, Author
Aakash Maurya
Senior Developer, C# Corner MVP, Speaker
Ankit Sharma
Senior Software Engineer, C# Corner MVP, Author
Mangesh Gaherwar
Team Lead, C# Corner MVP, Author
Viral Jain
Technical Consultant, C# Corner MVP, Author
Bhasker Das
Solution Architect, Evangelist
Manish Dwivedi
Associate Project Manager
Ck Nitin
Programmer, Author
Rohit Gupta
Technical Trainer, Author
Manish Tewatia
Full-stack Marketer, UX Designer
Bhavya Gaur
Technical Illustrator
Rohit Tomar
SEO/SMO Expert
Web Track
Cloud & Data Track
Dev Track
Registration & Breakfast
Future of Desktop Apps with JS (ElectronJs)
Nitin Pandit
Building Serverless Microservices Using Microsoft Azure
Vithal Wadje
Innovating RPA: A Robot for Every Person
Stephen Simon
Managing Cloud Storage Accounts using Logic Apps
Viknaraj Manogararajah
Data visualization using Python
Sekhar Srinivasan
Going Cross platform with AR Foundation
Vivek Sharma
Keynote
Managing your Azure dependencies in ASP.NET Core apps using VS
Bala Chirtsabesan
Securing Applications on Intelligent Azure
Abhishek Mishra
Getting started with Blazor the Framework of Future
S Ravi Kumar
Lunch
Build Progressive Web Apps using Angular 9
Debasis Saha
Build and deploy to any platform using Azure DevOps
Chervine Bhiwoo
Deep Dive in Azure Service Bus
Akshay Patel
Build a Native Mobile Application using React Native and JavaScript
Joseph Guadagno
Making sense of Web Job, Web Job SDK and Functions in Azure
Prakash Tripathi
CloudFront Distribution in AWS
Viral Jain
Tea Break
Introduction to PowerBI
Aakash Maurya
Build Advanced SPFx solutions with React and Graph API
Siddharth Vaghasia
Build Business Intelligence Analyst (BIA) Skills
Sundaram Subramanian
Deep dive of Power Platform – AI BUILDER
Prasham Sabadra
Panel 1
What's new in SharePoint development
Vipul Jain
Build a SSO (Single Sign On) based Native JavaScript application with Microsoft Identity within 10 minutes
Manoj Mittal
Panel 2
Applications and working of AI
Veena Sarda
Deploying serverless API's with .Net core 3.0 on AWS & Azure
Amey Vartak
Panel 3
Blockchain with .NET Core (Ark)
Anshu Kumari
Closing Note & Prize Distribution
Dev Track
Cloud Track
Architecture Track
Emerging Tech Track
Registration & Breakfast
Creating Full-Stack Web Apps Using Server-Side Blazor
Ankit Sharma
Real time face recognition with MS Cognitive Services
Niloshima Srivastava
Building Scalable APIs with GraphQL
Jeetendra Gund
Future of development with AI and Blockchain
Navdeep Garg
Debugging Tips and Tricks with Visual Studio 2019
Joseph Guadagno
Azure Containers
Abhishek Kant
Enterprise Architecture
Naveen Sharma
Bot Framework - learn it fast and look like a boss!
Allen O’Neill
Keynote
.Net Core & C# 8 Performance
David McCarter
Working with Azure kubernetes services
Ritesh Modi
Becoming an Architect
Vidyavrat Agarwal
Why Techies Need to Learn Product Management
Saurabh Jain
Lunch
Build a rules engine in .Net Core
Sanjay Vyas
Building CI and CD Pipeline using Azure DevOps
Sandeep Soni
Entity Framework Core - Tips and Tricks, Performance Optimization, and Tuning
Bassam Alugili
Hacking your way into Data Science
Sanket Verma
Speed up your .Net Core Website
Sourabh Somani
Azure
Magnus Mårtensson
Demystifying Open Distro for Elasticsearch
Suman Debnath
Future of Data
Shivam Ahuja
Tea Break
gRPC with C# and .Net Core
Mangesh Gaherwar
Panel 1
Essentials of Cloud security
Parveen Malik
Power platform and Dynamics 365
Deepesh Somani
Microservices - the gRPC Way
Viswanatha Swamy
Panel 2
Reserved
Reserved
Closing Note & Prize Distribution
Using Azure Firewall to Secure .NET Deployments
A .NET application may include APIs, web front ends, background workers, databases, storage accounts, and messaging services spread across several Azure networks. Each component increases the number of paths that must be controlled. Azure Firewall provides a centralized, stateful inspection point for managing those paths while keeping deployment policies consistent across environments.
Security teams can use it to filter outbound internet traffic, restrict access between application tiers, publish selected services through controlled entry points, and collect network activity for investigation. When combined with private endpoints, network security groups, managed identities, and secure deployment pipelines, it becomes part of a broader defense strategy rather than a standalone perimeter device.
The most effective implementation begins with the application’s communication map. A .NET API may need access to Azure Key Vault, SQL Database, Blob Storage, an identity provider, package feeds, and a message broker. Explicitly identifying those dependencies makes it possible to replace broad network access with narrowly defined rules.
Why network traffic deserves application-level attention
Many .NET deployments start with a simple virtual network design and gradually acquire additional resources. An application may initially expose a single HTTPS endpoint, then add administration tools, reporting services, worker processes, and integrations with external systems. If every subnet can reach the internet and every service can communicate freely, a compromised component has too much room to move.
Azure Firewall allows architects to define traffic policy at a central location. Network rules can control IP addresses and ports, application rules can filter fully qualified domain names for HTTP and HTTPS traffic, and DNAT rules can publish carefully selected internal services. This separation makes policies easier to review than a collection of disconnected rules on individual virtual machines.
The firewall should complement, rather than replace, other Azure controls. Network security groups remain useful for subnet and network-interface filtering. Azure Web Application Firewall protects web applications from attacks such as SQL injection and cross-site scripting. Identity controls protect access to resources and administrative operations. Each service addresses a different part of the threat surface.
Building a hub-and-spoke deployment model
A hub-and-spoke topology places shared security and connectivity services in a central hub virtual network. Azure Firewall resides in the hub, while application environments occupy separate spoke networks. User-defined routes direct outbound traffic from the spokes to the firewall, allowing development, staging, and production workloads to follow the same inspection model without merging their application resources.
For a .NET solution, one spoke might contain an ASP.NET Core API and an App Service integration, while another hosts data processing workers or containerized services. Peering connects the networks, but routing and firewall policy determine which flows are permitted. Production can receive stricter rules than development while still using the same architectural pattern.
Private endpoints reduce exposure for Azure SQL, Storage, Key Vault, and other platform services by assigning them private addresses inside a virtual network. DNS must be designed alongside those endpoints. If an application resolves a service name to a public address when private access is intended, traffic may bypass the expected route or fail unexpectedly. Private DNS zones, linked virtual networks, and testing from the actual application subnet are essential.
Choosing rules for .NET workloads
Firewall policy should be based on required flows rather than a large allowlist assembled after deployment failures. Start with the source subnet, destination, protocol, port, and business purpose. A worker that retrieves secrets from Key Vault has a different requirement from an API that calls a payment provider. Recording that difference makes future audits and troubleshooting much easier.
Application rules are useful when outbound .NET services need access to known domains. For example, a deployment may allow HTTPS connections to a package repository, identity endpoint, telemetry service, or external API. Network rules are better suited to private addresses, database ports, and internal service communication. FQDN filtering should be tested carefully because some cloud services use several hostnames or dynamically resolved endpoints.
Threat intelligence mode can alert on or deny traffic associated with known malicious destinations. TLS inspection, available with the appropriate Azure Firewall tier and design, offers deeper visibility into encrypted traffic but introduces certificate management, compatibility testing, and operational overhead. It should be enabled where the security benefit justifies the effect on application behavior and privacy requirements.
| Control | Primary purpose | Example for a .NET deployment | Important consideration |
|---|---|---|---|
| Azure Firewall | Central traffic inspection and routing | Restrict API egress and control spoke-to-spoke flows | Requires deliberate routes and policy ownership |
| Network security group | Subnet and interface filtering | Permit only API-to-worker traffic on approved ports | Rules are distributed across network resources |
| Web Application Firewall | HTTP attack protection | Inspect requests reaching an ASP.NET Core application | Focuses on web-layer threats, not general egress |
| Private endpoint | Private access to Azure services | Connect privately to SQL, Storage, or Key Vault | DNS configuration is part of the implementation |
| Managed identity | Passwordless resource authentication | Let a worker read secrets or storage data | Permissions must be scoped and reviewed |
| Azure Monitor and Firewall logs | Detection and investigation | Identify denied calls or unusual outbound destinations | Logs need retention, alerts, and operational ownership |
Connecting firewall policy with deployment automation
Infrastructure as code helps keep firewall configuration aligned with application environments. Bicep, ARM templates, or Terraform can define firewall policies, route tables, private DNS zones, and diagnostic settings alongside the resources they protect. Version control provides a history of changes and allows security reviewers to examine a proposed rule before it reaches production.
A pipeline should validate policy syntax, detect overlapping or shadowed rules, and test essential connectivity. Automated checks can confirm that an API reaches its database through the intended private route, that a worker cannot access an unauthorized subnet, and that required external endpoints remain available. A deployment that succeeds at the resource level but fails at runtime because of an omitted egress rule is still an incomplete deployment.
Use separate policy assignments or rule collections for different environments. Development may need access to test tools and package feeds, while production should permit only documented dependencies. Approval gates are especially valuable for rules involving public inbound exposure, broad destination ranges, administrative ports, or TLS inspection.
Messaging is another area where network assumptions affect application reliability. A worker that communicates through Azure Service Bus should use private connectivity or tightly controlled endpoints where feasible, and its identity should receive only the required queue or topic permissions. Teams designing asynchronous systems can also review message queuing patterns when deciding which traffic belongs inside the protected network path.
Managing inbound access and application exposure
Public access should be limited to services that genuinely need to receive internet traffic. A common pattern places Azure Application Gateway with Web Application Firewall in front of an ASP.NET Core application, while Azure Firewall governs broader network traffic and outbound connectivity. This arrangement gives HTTP requests an application-aware inspection layer and gives network flows a centralized control point.
When a public load balancer or another edge service forwards traffic into a virtual network, the permitted path must be explicit. DNAT can map a public address and port to a private destination, but publishing a port does not make the target secure by itself. The application still needs authentication, authorization, input validation, rate controls, and secure headers.
Administrative access deserves a separate design. Avoid opening RDP or SSH broadly to the internet. Azure Bastion, privileged access workflows, just-in-time access, and identity-based administration reduce the chance that a management endpoint becomes the easiest route into the environment. For deployment agents, use private connectivity or self-hosted runners with narrowly scoped permissions instead of permanent public management access.
Observability, testing, and operational response
A firewall policy without useful telemetry is difficult to maintain. Enable Azure Firewall application rule, network rule, DNS proxy, and threat intelligence logs as appropriate. Route them to Log Analytics or another approved destination, then create queries and alerts around denied production traffic, repeated connection attempts, unexpected destinations, and sudden changes in outbound volume.
Diagnostic data should be correlated with application logs. A .NET service may report a timeout while the firewall records a denied connection, or the application may show a DNS failure when a private endpoint zone is misconfigured. Correlation IDs, consistent timestamps, and centralized dashboards help engineers distinguish a code defect from a routing or policy problem.
Testing should cover ordinary releases and failure scenarios. Verify that permitted dependencies work after a firewall policy change, that denied traffic is actually blocked, and that a compromised test workload cannot reach protected subnets. Load testing can reveal whether throughput, scaling, or latency requirements demand a different firewall tier or additional capacity planning.
Review rules regularly for stale destinations and temporary exceptions. Every rule should have an owner, purpose, environment scope, and review date. Removing unused access reduces policy complexity and makes meaningful alerts easier to recognize.
Practical safeguards for production readiness
Use the following safeguards when preparing a secure .NET deployment:
- Route spoke egress through a centralized Azure Firewall and document every required exception.
- Keep databases, storage, Key Vault, and messaging services on private connectivity whenever the architecture supports it.
- Combine firewall rules with network security groups, Web Application Firewall policies, managed identities, and least-privilege permissions.
- Store firewall and network configuration in infrastructure-as-code repositories with peer review and deployment approvals.
- Send diagnostic logs to a monitored workspace and test alerts using both allowed and denied traffic.
- Separate development, staging, and production policies so temporary experimentation cannot become permanent exposure.
A phased rollout reduces risk. Begin by observing traffic and inventorying dependencies, then introduce explicit rules in a nonproduction environment. After application teams resolve blocked calls and update documentation, promote the policy through controlled stages. This process creates a reliable baseline before production enforcement begins.
Security ownership should be shared across developers, platform engineers, and operations teams. Developers understand service dependencies, platform teams manage routing and policy, and operations teams respond to telemetry. Clear ownership prevents firewall changes from becoming either an unreviewed application workaround or an isolated infrastructure task.
Treat Azure Firewall as a living part of the .NET platform. Define the intended traffic paths, express them as reviewed policy, deploy them through automation, and monitor the results continuously. Apply these practices to your next Azure architecture review and turn network security from a late deployment obstacle into an enforceable part of delivery.
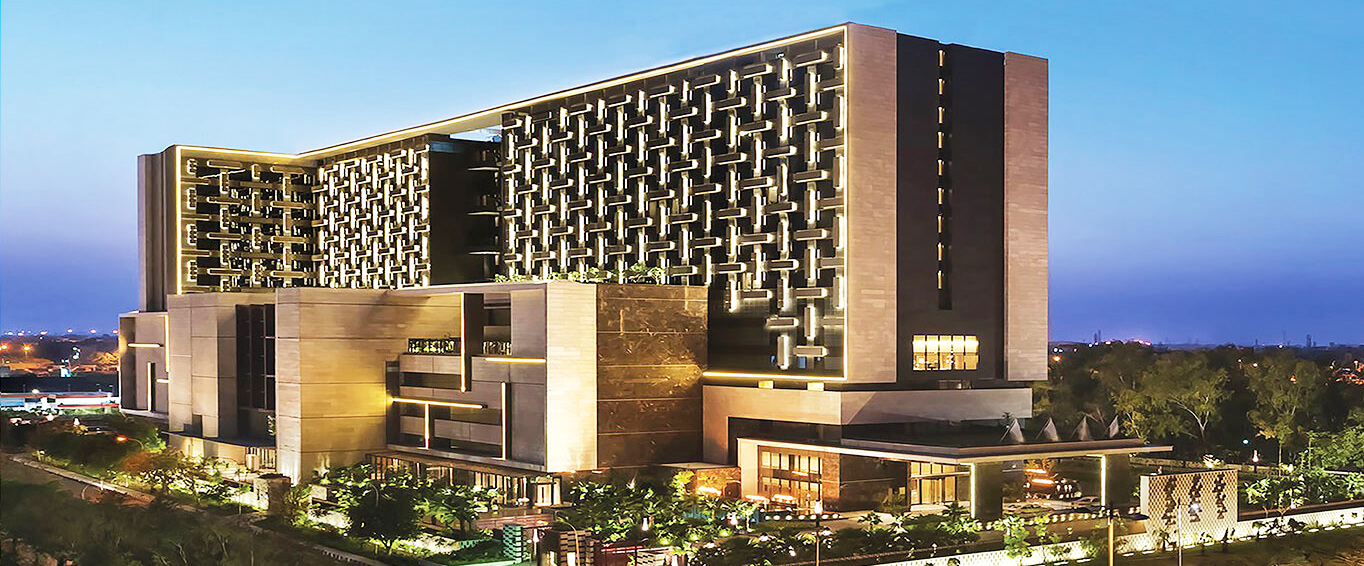
1, CBD, Maharaj Surajmal Road, Near Yamuna Sports Complex, Delhi, 110032
GENERAL QUERIES
Manish Tewatia
manish@csharpcon.com
+91-9718-431-042
TICKET QUERIES
Atul Gupta
conference@csharpcon.com
+91-9910-125-804