Presents
Magnus Mårtensson
Microsoft Regional Director, Azure MVP, CEO Loftysoft
Avirag Jain
Director & CTO R Systems
Mahesh Chand
Founder C# Corner, CEO Mindcracker
Chris Gali
CEO & Co-Founder Graphite
Subinder Khurana
Chief Architect StoryProcess, Founder NASSCOM DeepTech Club
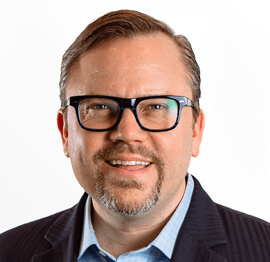
Bryan Rishforth
Investor, Chairman Graphite
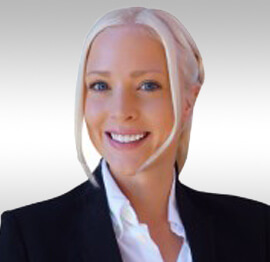
Bryn Everson
Director Biz Dev Graphite
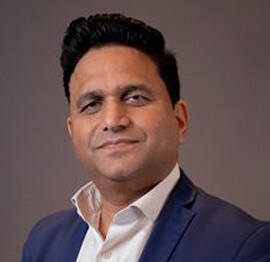
Raj Tiwari
Digital Transformation Leader, Futurist and Visionary
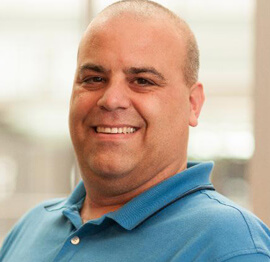
Joseph Guadagno
Microsoft MVP, Lead Quicken Loans
Nikita Sachdev
Entrepreneur, Blockchain Enthusiast & Advisor, Social Media Influencer
Doug Wagner
COO & Founder Adapt Technical Group
Ritesh Modi
Architect, Senior Evangelist, Cloud Architect
Crystal Wenrick
Director Communications Mindcracker
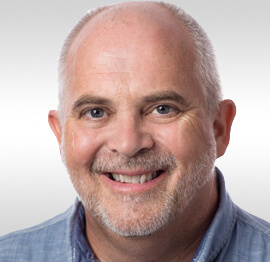
Allen O’Neill
Microsoft MVP, Consulting Engineer/Architect
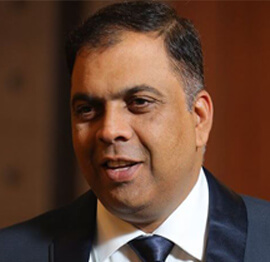
Praveen Kumar
CEO MCN Solutions
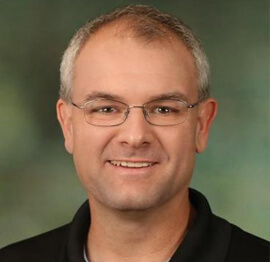
Chris Love
Founder Love2Dev, Microsoft MVP, Author
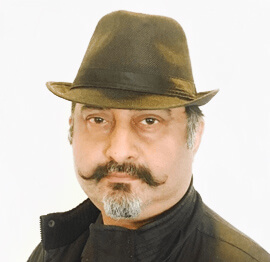
Sanjay Vyas
Microsoft Regional Director, Microsoft MVP, Founder & CEO SkillLabs Technologies
Veena Sarda
Deep Learning Consultant, Author
Sekhar Srinivasan
C# Corner MVP, Microsoft Certified Trainer, Pluralsight Author
Lalit Bansal
Founder & CEO - EIY SYS
Navdeep Garg
CEO Revinfotech
Prakash Tripathi
Tech Manager/Leader, Microsoft MVP, Blogger
Bhavna Jain
Breakthrough Consultant
Naveen Sharma
Enterprise Architect, Leadership Coach, Author
Vidya Vrat Agarwal
Principal Architect, Microsoft MVP, Author
Sheetal Agarwal
Founder Clownselors, Medical Clown, Trainer
Abhishek Kant
Founder GTM Catalyst
Vishnu Saran
Founder & CEO VoiceQube
Sandeep Soni
Founder & CEO Deccansoft, Microsoft Certified Trainer
Parveen Malik
AVP InfoSec & Vulnerability Management, Information Security Expert
Nitin Pandit
Microsoft MVP, Developer Evangelist, Author
Niloshima Srivastava
C# Corner MVP, Tech Architect, Trainer, Blogger
Bala Chirtsabesan
Senior Software Engineer at Microsoft, Author
Manoj Mittal
Sr. Technical Architect, C# Corner MVP, Author
Chandni Di
Co-Founder Voice of Slum
Vithal Wadje
Technical Lead, Microsoft MVP, Author
Shivam Ahuja
Founder SkillCircle, Business Mentor
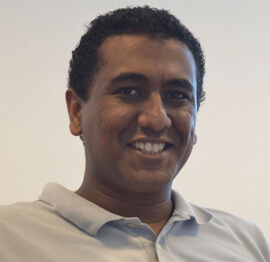
Chervine Bhiwoo
Solution Architect, Microsoft MVP, Author
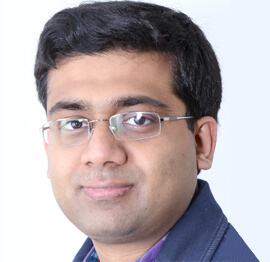
Saurabh Jain
Vice President Paytm, Founder Fun2Do Labs, Author
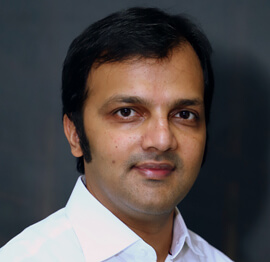
Vinay Solanki
Head IoT at Lenovo, Founder IoT-NCR
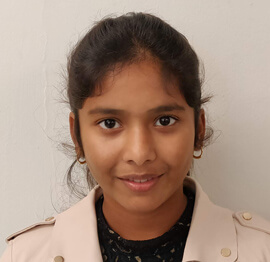
Anshu kumari
Founder Blockchainkids, Inventor, Trainer
Amit Singal
CEO Startup Buddy
Dev Pratap
Co-Founder & CEO Voice of Slum
Amey Vartak
Technology Consultant, Full Stack Developer, C# Corner MVP, Author
Viswanatha Swamy
Principal Software Engineer, C# Corner MVP, Author
Sanket Verma
Research Engineer @ Ballistics (Forensics) and Chair, PyData Delhi
Sourabh Somani
Lead Developer, Microsoft MVP, Author
Abhishek Mishra
Software Architect, C# Corner MVP, Author
Siddharth Vaghasia
Technical Consultant, C# Corner MVP, Blogger
Bassam Alugili
Senior Software Specialist, Database Expert
S Ravi Kumar
Solution Architect, C# Corner MVP, Author
Sundaram Subramanian
Full Stack Developer, C# Corner MVP, Speaker
Deepesh Somani
Solution Architect, Microsoft MVP, Author
Debasis Saha
Technical Project Manager, C# Corner MVP, Blogger, Author
Vipul Jain
Software Architect, C# Corner MVP, Author
Akshay Patel
Technical Architect, Microsoft Certified Trainer, C# Corner MVP, Author
Stephen Simon
RPA Developer, Evangelist, Author
Vivek Sharma
Founder Kingster636, AR/VR Specialist
Jeetendra Gund
Technical Lead, C# Corner MVP, Author
Sujal Beniwal
AI Enthusiast, Student
M Viknaraj
Microsoft MVP, Azure Architect, Author
Prasham Sabadra
Software Architect, C# Corner MVP, Trainer, Author
Aakash Maurya
Senior Developer, C# Corner MVP, Speaker
Ankit Sharma
Senior Software Engineer, C# Corner MVP, Author
Mangesh Gaherwar
Team Lead, C# Corner MVP, Author
Viral Jain
Technical Consultant, C# Corner MVP, Author
Bhasker Das
Solution Architect, Evangelist
Manish Dwivedi
Associate Project Manager
Ck Nitin
Programmer, Author
Rohit Gupta
Technical Trainer, Author
Manish Tewatia
Full-stack Marketer, UX Designer
Bhavya Gaur
Technical Illustrator
Rohit Tomar
SEO/SMO Expert
Web Track
Cloud & Data Track
Dev Track
Registration & Breakfast
Future of Desktop Apps with JS (ElectronJs)
Nitin Pandit
Building Serverless Microservices Using Microsoft Azure
Vithal Wadje
Innovating RPA: A Robot for Every Person
Stephen Simon
Managing Cloud Storage Accounts using Logic Apps
Viknaraj Manogararajah
Data visualization using Python
Sekhar Srinivasan
Going Cross platform with AR Foundation
Vivek Sharma
Keynote
Managing your Azure dependencies in ASP.NET Core apps using VS
Bala Chirtsabesan
Securing Applications on Intelligent Azure
Abhishek Mishra
Getting started with Blazor the Framework of Future
S Ravi Kumar
Lunch
Build Progressive Web Apps using Angular 9
Debasis Saha
Build and deploy to any platform using Azure DevOps
Chervine Bhiwoo
Deep Dive in Azure Service Bus
Akshay Patel
Build a Native Mobile Application using React Native and JavaScript
Joseph Guadagno
Making sense of Web Job, Web Job SDK and Functions in Azure
Prakash Tripathi
CloudFront Distribution in AWS
Viral Jain
Tea Break
Introduction to PowerBI
Aakash Maurya
Build Advanced SPFx solutions with React and Graph API
Siddharth Vaghasia
Build Business Intelligence Analyst (BIA) Skills
Sundaram Subramanian
Deep dive of Power Platform – AI BUILDER
Prasham Sabadra
Panel 1
What's new in SharePoint development
Vipul Jain
Build a SSO (Single Sign On) based Native JavaScript application with Microsoft Identity within 10 minutes
Manoj Mittal
Panel 2
Applications and working of AI
Veena Sarda
Deploying serverless API's with .Net core 3.0 on AWS & Azure
Amey Vartak
Panel 3
Blockchain with .NET Core (Ark)
Anshu Kumari
Closing Note & Prize Distribution
Dev Track
Cloud Track
Architecture Track
Emerging Tech Track
Registration & Breakfast
Creating Full-Stack Web Apps Using Server-Side Blazor
Ankit Sharma
Real time face recognition with MS Cognitive Services
Niloshima Srivastava
Building Scalable APIs with GraphQL
Jeetendra Gund
Future of development with AI and Blockchain
Navdeep Garg
Debugging Tips and Tricks with Visual Studio 2019
Joseph Guadagno
Azure Containers
Abhishek Kant
Enterprise Architecture
Naveen Sharma
Bot Framework - learn it fast and look like a boss!
Allen O’Neill
Keynote
.Net Core & C# 8 Performance
David McCarter
Working with Azure kubernetes services
Ritesh Modi
Becoming an Architect
Vidyavrat Agarwal
Why Techies Need to Learn Product Management
Saurabh Jain
Lunch
Build a rules engine in .Net Core
Sanjay Vyas
Building CI and CD Pipeline using Azure DevOps
Sandeep Soni
Entity Framework Core - Tips and Tricks, Performance Optimization, and Tuning
Bassam Alugili
Hacking your way into Data Science
Sanket Verma
Speed up your .Net Core Website
Sourabh Somani
Azure
Magnus Mårtensson
Demystifying Open Distro for Elasticsearch
Suman Debnath
Future of Data
Shivam Ahuja
Tea Break
gRPC with C# and .Net Core
Mangesh Gaherwar
Panel 1
Essentials of Cloud security
Parveen Malik
Power platform and Dynamics 365
Deepesh Somani
Microservices - the gRPC Way
Viswanatha Swamy
Panel 2
Reserved
Reserved
Closing Note & Prize Distribution
Building an API gateway with YARP and .NET 8
Modern applications rarely expose every service directly to clients. A browser, mobile app or partner integration usually needs one reliable entry point that can route requests, apply security policies, standardise responses and protect internal services. For teams building on ASP.NET Core, YARP provides a practical way to create that reverse proxy without introducing a separate gateway product.
YARP, or Yet Another Reverse Proxy, is a .NET library developed by Microsoft. Combined with .NET 8, it supports a flexible API gateway architecture with route matching, load balancing, health checks, transforms and middleware. This approach suits Australian development teams managing cloud workloads in Sydney or Melbourne, where latency, data residency and operational simplicity can influence gateway design.
| Capability | YARP with .NET 8 | Managed API gateway | Nginx or similar proxy | Custom proxy |
|---|---|---|---|---|
| .NET integration | Excellent | Usually adapter-based | External process | Depends on implementation |
| Routing flexibility | High | High | High | Potentially high |
| Built-in cloud features | Requires configuration | Broad | Requires additional services | Must be developed |
| Operational control | Full application-level control | Provider-controlled | Infrastructure-focused | Full control |
| Best fit | .NET microservices and tailored gateways | Large enterprise platforms | Standard reverse-proxy workloads | Specialised protocols or policies |
Why an API gateway belongs at the edge
An API gateway sits between external consumers and internal services. Instead of publishing separate endpoints for orders, accounts, payments and notifications, a client can call a consistent public host. The gateway forwards each request to the appropriate backend while keeping internal hostnames, ports and deployment details private.
This boundary is useful for more than routing. Authentication, request correlation, rate limiting, header normalisation, CORS, TLS termination and access logging can be handled centrally. A gateway can also shield older services from public exposure while a platform team gradually modernises them.
YARP is especially attractive when the delivery team already uses C#, ASP.NET Core dependency injection, Microsoft Entra ID and Azure. Developers can extend the proxy with normal .NET middleware and services rather than learning a separate scripting language. It remains important to keep the gateway focused: business rules and domain workflows belong in application services, not in route configuration.
For an Australian service, deployment location deserves early attention. Hosting the gateway and primary APIs in an Australian Azure region can reduce round-trip time for users in Sydney, Brisbane and Melbourne. It may also support contractual or regulatory expectations around where customer information is processed, although the gateway itself does not automatically guarantee compliance with the Privacy Act or Australian Privacy Principles.
Creating the .NET 8 gateway project
Start with a standard ASP.NET Core application and add the YARP package:
dotnet new web -n Gateway
cd Gateway
dotnet add package Yarp.ReverseProxy
A minimal Program.cs can load routes and clusters from configuration:
var builder = WebApplication.CreateBuilder(args);

builder.Services
    .AddReverseProxy()
    .LoadFromConfig(builder.Configuration.GetSection("ReverseProxy"));

var app = builder.Build();

app.UseHttpsRedirection();
app.MapReverseProxy();

app.Run();
The AddReverseProxy call registers YARP services, while LoadFromConfig reads the routing model from appsettings.json. MapReverseProxy adds the endpoint that receives matching requests and forwards them to a destination.
A basic configuration might look like this:
{
  "ReverseProxy": {
    "Routes": {
      "catalog-route": {
        "ClusterId": "catalog-cluster",
        "Match": {
          "Path": "/api/catalog/{**catch-all}"
        }
      }
    },
    "Clusters": {
      "catalog-cluster": {
        "Destinations": {
          "catalog-service": {
            "Address": "https://localhost:7001/"
          }
        }
      }
    }
  }
}
The route defines the public path, and the cluster defines one or more backend destinations. In a production environment, destination addresses should normally come from environment-specific configuration, service discovery or a managed platform rather than being hard-coded into source control.
Designing routes, clusters and transforms
YARP separates route matching from destination selection. This distinction makes the gateway easier to evolve. A route can match a path, HTTP method, host or header, while a cluster can contain several destinations and a load-balancing policy. Multiple public routes may therefore share the same backend cluster.
Path transforms are useful when public and internal URL structures differ. For example, clients might call /api/orders/123, while an internal service expects /orders/123. A transform can remove or add a path prefix before forwarding the request. Header transforms can add correlation identifiers, preserve the original host or remove headers that should never reach an internal service.
A route with a transform could be configured as follows:
{
  "Routes": {
    "orders-route": {
      "ClusterId": "orders-cluster",
      "Match": {
        "Path": "/api/orders/{**remainder}"
      },
      "Transforms": [
        { "PathRemovePrefix": "/api" },
        { "RequestHeader": "X-Gateway", "Set": "yarp" }
      ]
    }
  }
}
Use explicit route conventions. Keep public versioning such as /api/v1 stable, and avoid exposing internal service names in client-facing URLs. In a multi-team environment, consistent naming helps developers in Melbourne or Perth understand ownership when they inspect logs and deployment settings.
YARP also supports health checks and load balancing. A cluster can contain several instances of a service, allowing traffic to be distributed across containers, virtual machines or App Service deployments. Health monitoring should reflect actual service readiness rather than simply confirming that a process is running.
Adding authentication, authorisation and resilience
Authentication should be enforced at the correct boundary. A gateway can validate bearer tokens issued by Microsoft Entra ID or another identity provider before forwarding requests. ASP.NET Core authentication and authorisation middleware can protect all routes or selected route groups.
A typical setup registers JWT bearer authentication:
builder.Services.AddAuthentication("Bearer")
    .AddJwtBearer("Bearer", options =>
    {
        options.Authority = builder.Configuration["Identity:Authority"];
        options.Audience = "api";
    });

builder.Services.AddAuthorization();

var app = builder.Build();

app.UseAuthentication();
app.UseAuthorization();
app.MapReverseProxy();
The exact order and policy design should match the application’s security model. Some systems pass the original token to downstream services so each service can perform its own authorisation. Others exchange the external token for a narrower internal credential. Avoid treating authentication at the gateway as a substitute for service-level authorisation.
Resilience features require equal care. Timeouts prevent a slow dependency from consuming every gateway thread, while retries can help with short-lived network faults. Retrying non-idempotent operations such as payments or order creation can create duplicate actions, so retry policies should consider the HTTP method and business semantics.
Useful gateway controls include:
- Request timeouts and cancellation propagation
- Rate limits for public and partner-facing endpoints
- Circuit breakers for failing downstream services
- Maximum request and response sizes
For Australian consumer traffic, rate limiting can help absorb sudden demand from a campaign, sporting event or retail promotion. It should be paired with clear client responses such as HTTP 429 and useful retry guidance rather than silently dropping requests.
Observability and production operations
A gateway becomes a central diagnostic point, so its telemetry must be designed before launch. Record structured logs with a correlation ID, route name, destination, status code, duration and failure category. Do not log access tokens, passwords, payment details or unnecessary personal information.
OpenTelemetry integrates well with modern .NET applications and can export traces and metrics to Azure Monitor, Application Insights or another observability platform. Distributed tracing allows an engineer to follow a request from the gateway to an orders service, database and external provider. This is far more useful than a single “502 Bad Gateway” message.
Health endpoints should distinguish between process health and dependency readiness. A liveness check can confirm that the gateway is running, while a readiness check can indicate whether it can safely accept traffic. Kubernetes, Azure Container Apps and other hosting platforms use these signals to make deployment decisions.
Operational checks worth defining include:
- Gateway latency by route and HTTP status
- Upstream failures, timeouts and connection errors
- Requests rejected by authentication or rate limits
- Destination health and load distribution
In Australia, teams should verify that monitoring data is stored in an approved region and that retention settings match organisational policy. A company serving customers across New South Wales and Victoria may also need alert coverage outside standard office hours, especially when the gateway fronts payments, logistics or public-sector services.
Securing configuration and deployment
Configuration should be externalised across development, testing and production. Local developers can use user secrets or a development settings file, while production deployments can use Azure App Configuration, Key Vault, managed identities or environment variables. Never place client secrets, certificates or database credentials in appsettings.json committed to a repository.
TLS should terminate at a trusted edge such as Azure Front Door, Application Gateway or the hosting platform, depending on the network design. Encrypting the connection from the edge to YARP and from YARP to internal services provides stronger protection across the entire path. Internal services should still validate identity and apply their own authorisation rules.
A production pipeline should build, test and scan the gateway as an ordinary .NET 8 application. Include route tests, authentication tests, transform tests and failure scenarios. Contract tests can confirm that the gateway continues to produce the paths and headers expected by downstream services.
Blue-green or rolling deployments reduce risk when changing routes. A new route should first target a test destination or limited audience. Logs and metrics can then confirm that forwarding, latency and authentication behave as expected before traffic is expanded. This staged approach is valuable for teams supporting customers across Australian time zones, where a fault introduced during a late Sydney deployment may affect users nationwide.
Extending YARP without creating a bottleneck
YARP can be extended through custom transforms, destination resolvers, load-balancing policies and proxy middleware. These extension points are powerful, but every custom feature increases the gateway’s maintenance surface. Prefer built-in configuration where it expresses the requirement clearly, and add code only when a reusable policy cannot be configured.
A custom transform may add tenant context, rewrite a header or adapt a legacy backend. It should validate input and avoid trusting client-supplied identity headers. If a downstream service needs a tenant identifier, derive it from a verified token or trusted server-side lookup rather than accepting arbitrary values from the request.
The gateway should remain stateless wherever possible. Stateless instances can scale horizontally behind a load balancer and can be replaced during deployments without session migration. Shared state, such as throttling counters or temporary tokens, should be managed by a dedicated service with clear availability characteristics.
Before releasing a YARP gateway, check these implementation details:
- Confirm every public route has an authentication and authorisation policy
- Test unhealthy destinations and slow downstream responses
- Verify forwarded headers and original client IP handling
- Review sensitive data in logs, traces and error responses
A well-designed .NET 8 gateway gives developers a controlled edge for APIs while preserving the freedom to evolve internal services. YARP is most effective when paired with disciplined route ownership, secure configuration, meaningful telemetry and realistic load testing. That combination supports a maintainable platform for cloud-native applications, whether the workload serves a local Australian business or a distributed global customer base.
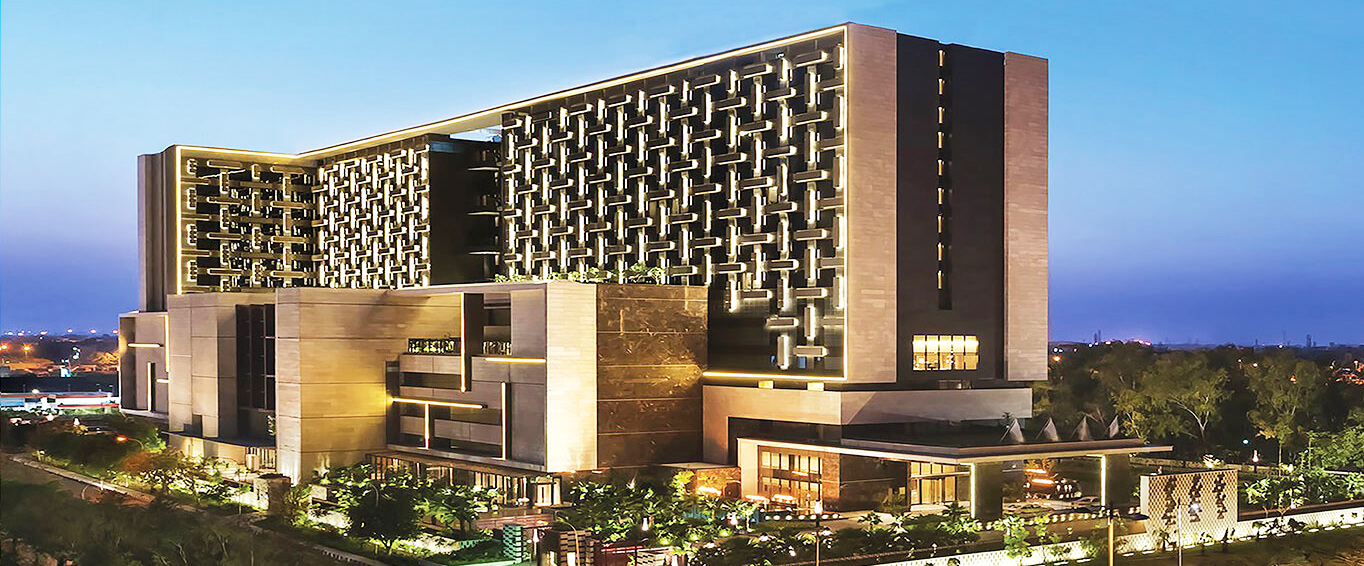
1, CBD, Maharaj Surajmal Road, Near Yamuna Sports Complex, Delhi, 110032
GENERAL QUERIES
Manish Tewatia
manish@csharpcon.com
+91-9718-431-042
TICKET QUERIES
Atul Gupta
conference@csharpcon.com
+91-9910-125-804