Presents
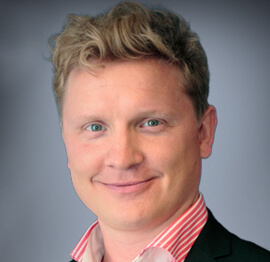
Magnus Mårtensson
Microsoft Regional Director, Azure MVP, CEO Loftysoft
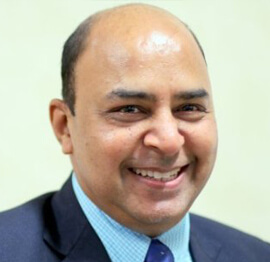
Avirag Jain
Director & CTO R Systems
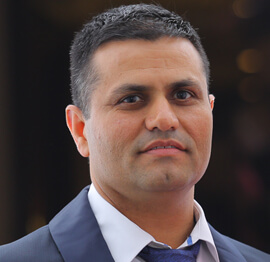
Mahesh Chand
Founder C# Corner, CEO Mindcracker
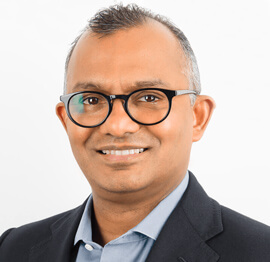
Chris Gali
CEO & Co-Founder Graphite
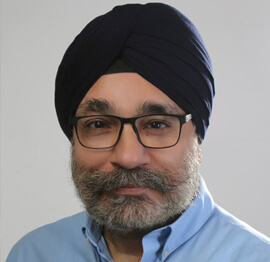
Subinder Khurana
Chief Architect StoryProcess, Founder NASSCOM DeepTech Club
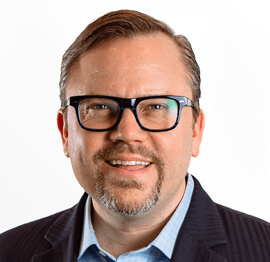
Bryan Rishforth
Investor, Chairman Graphite
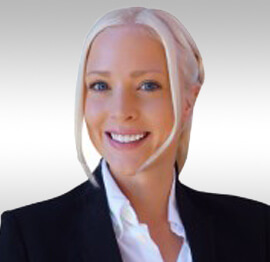
Bryn Everson
Director Biz Dev Graphite
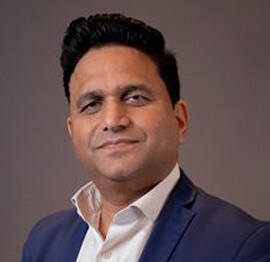
Raj Tiwari
Digital Transformation Leader, Futurist and Visionary
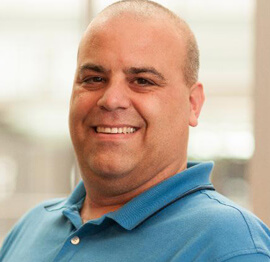
Joseph Guadagno
Microsoft MVP, Lead Quicken Loans
Nikita Sachdev
Entrepreneur, Blockchain Enthusiast & Advisor, Social Media Influencer
Doug Wagner
COO & Founder Adapt Technical Group
Ritesh Modi
Architect, Senior Evangelist, Cloud Architect
Crystal Wenrick
Director Communications Mindcracker
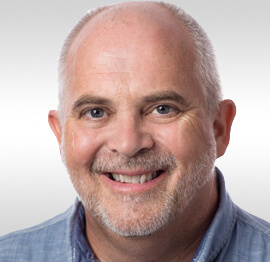
Allen O’Neill
Microsoft MVP, Consulting Engineer/Architect
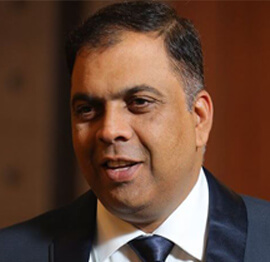
Praveen Kumar
CEO MCN Solutions
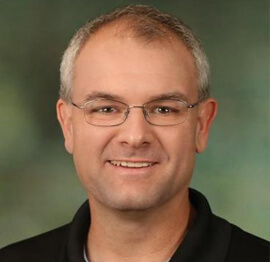
Chris Love
Founder Love2Dev, Microsoft MVP, Author
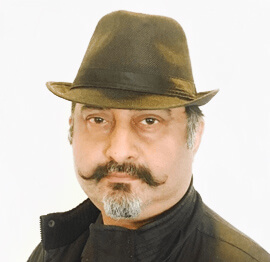
Sanjay Vyas
Microsoft Regional Director, Microsoft MVP, Founder & CEO SkillLabs Technologies
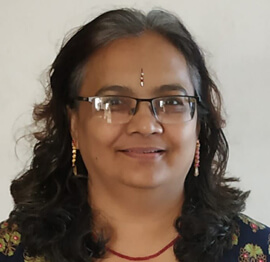
Veena Sarda
Deep Learning Consultant, Author
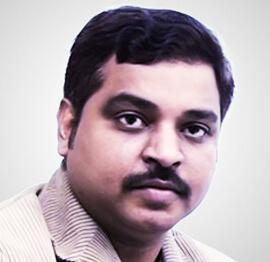
Sekhar Srinivasan
C# Corner MVP, Microsoft Certified Trainer, Pluralsight Author
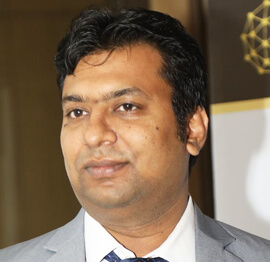
Lalit Bansal
Founder & CEO - EIY SYS
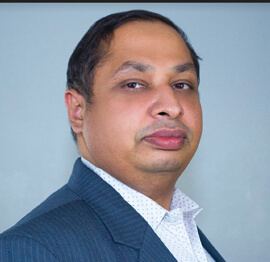
Navdeep Garg
CEO Revinfotech
Prakash Tripathi
Tech Manager/Leader, Microsoft MVP, Blogger
Bhavna Jain
Breakthrough Consultant
Naveen Sharma
Enterprise Architect, Leadership Coach, Author
Vidya Vrat Agarwal
Principal Architect, Microsoft MVP, Author
Sheetal Agarwal
Founder Clownselors, Medical Clown, Trainer
Abhishek Kant
Founder GTM Catalyst
Vishnu Saran
Founder & CEO VoiceQube
Sandeep Soni
Founder & CEO Deccansoft, Microsoft Certified Trainer
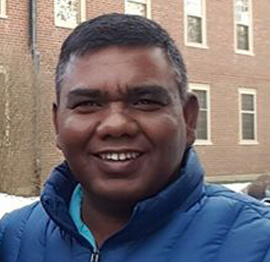
Parveen Malik
AVP InfoSec & Vulnerability Management, Information Security Expert
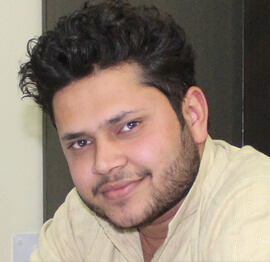
Nitin Pandit
Microsoft MVP, Developer Evangelist, Author
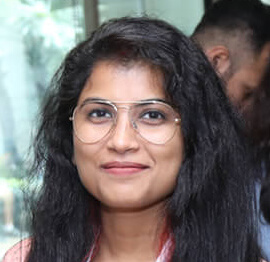
Niloshima Srivastava
C# Corner MVP, Tech Architect, Trainer, Blogger
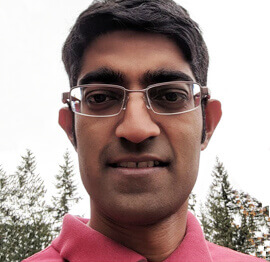
Bala Chirtsabesan
Senior Software Engineer at Microsoft, Author
Manoj Mittal
Sr. Technical Architect, C# Corner MVP, Author
Chandni Di
Co-Founder Voice of Slum
Vithal Wadje
Technical Lead, Microsoft MVP, Author
Shivam Ahuja
Founder SkillCircle, Business Mentor
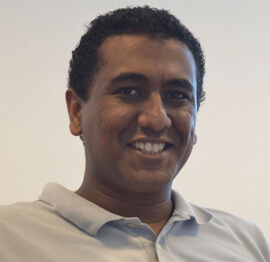
Chervine Bhiwoo
Solution Architect, Microsoft MVP, Author
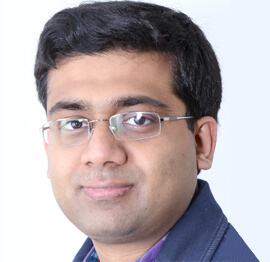
Saurabh Jain
Vice President Paytm, Founder Fun2Do Labs, Author
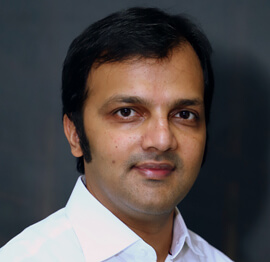
Vinay Solanki
Head IoT at Lenovo, Founder IoT-NCR
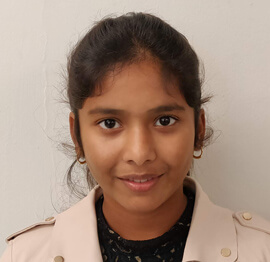
Anshu kumari
Founder Blockchainkids, Inventor, Trainer
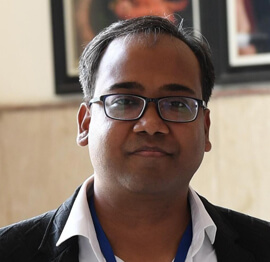
Amit Singal
CEO Startup Buddy
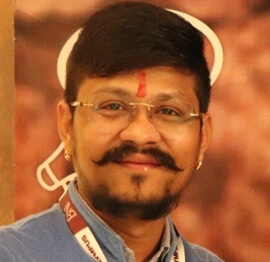
Dev Pratap
Co-Founder & CEO Voice of Slum
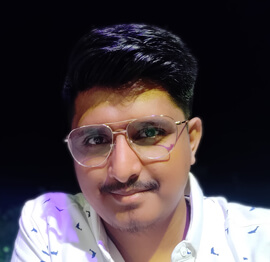
Amey Vartak
Technology Consultant, Full Stack Developer, C# Corner MVP, Author
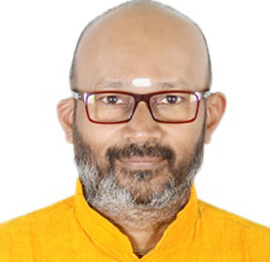
Viswanatha Swamy
Principal Software Engineer, C# Corner MVP, Author
Sanket Verma
Research Engineer @ Ballistics (Forensics) and Chair, PyData Delhi
Sourabh Somani
Lead Developer, Microsoft MVP, Author
Abhishek Mishra
Software Architect, C# Corner MVP, Author
Siddharth Vaghasia
Technical Consultant, C# Corner MVP, Blogger
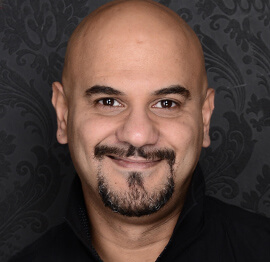
Bassam Alugili
Senior Software Specialist, Database Expert
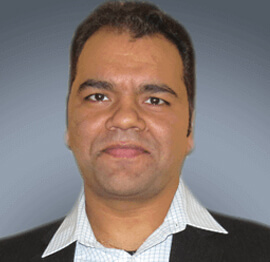
S Ravi Kumar
Solution Architect, C# Corner MVP, Author
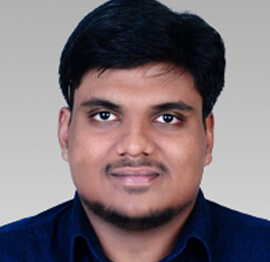
Sundaram Subramanian
Full Stack Developer, C# Corner MVP, Speaker
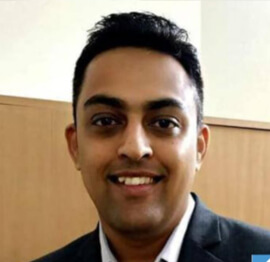
Deepesh Somani
Solution Architect, Microsoft MVP, Author
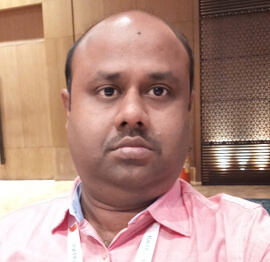
Debasis Saha
Technical Project Manager, C# Corner MVP, Blogger, Author
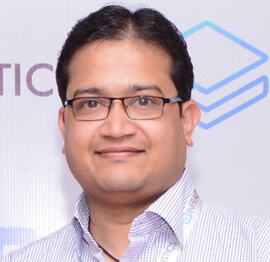
Vipul Jain
Software Architect, C# Corner MVP, Author
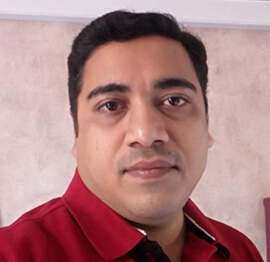
Akshay Patel
Technical Architect, Microsoft Certified Trainer, C# Corner MVP, Author
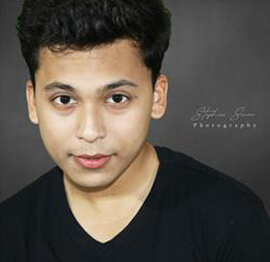
Stephen Simon
RPA Developer, Evangelist, Author
Vivek Sharma
Founder Kingster636, AR/VR Specialist
Jeetendra Gund
Technical Lead, C# Corner MVP, Author
Sujal Beniwal
AI Enthusiast, Student
M Viknaraj
Microsoft MVP, Azure Architect, Author
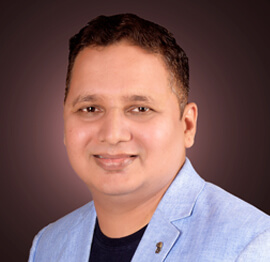
Prasham Sabadra
Software Architect, C# Corner MVP, Trainer, Author
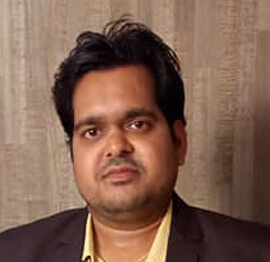
Aakash Maurya
Senior Developer, C# Corner MVP, Speaker
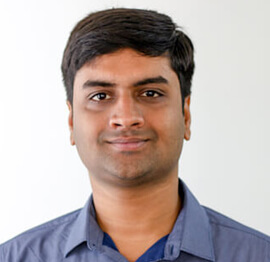
Ankit Sharma
Senior Software Engineer, C# Corner MVP, Author
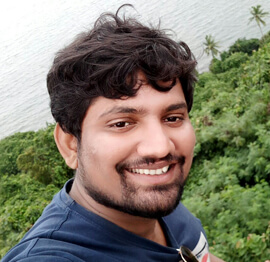
Mangesh Gaherwar
Team Lead, C# Corner MVP, Author
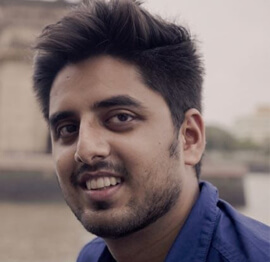
Viral Jain
Technical Consultant, C# Corner MVP, Author
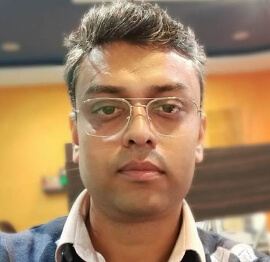
Bhasker Das
Solution Architect, Evangelist
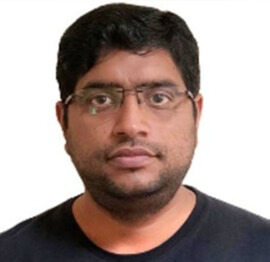
Manish Dwivedi
Associate Project Manager
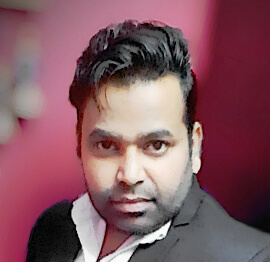
Ck Nitin
Programmer, Author
Rohit Gupta
Technical Trainer, Author
Manish Tewatia
Full-stack Marketer, UX Designer
Bhavya Gaur
Technical Illustrator
Rohit Tomar
SEO/SMO Expert
Web Track
Cloud & Data Track
Dev Track
Registration & Breakfast
Future of Desktop Apps with JS (ElectronJs)
Nitin Pandit
Building Serverless Microservices Using Microsoft Azure
Vithal Wadje
Innovating RPA: A Robot for Every Person
Stephen Simon
Managing Cloud Storage Accounts using Logic Apps
Viknaraj Manogararajah
Data visualization using Python
Sekhar Srinivasan
Going Cross platform with AR Foundation
Vivek Sharma
Keynote
Managing your Azure dependencies in ASP.NET Core apps using VS
Bala Chirtsabesan
Securing Applications on Intelligent Azure
Abhishek Mishra
Getting started with Blazor the Framework of Future
S Ravi Kumar
Lunch
Build Progressive Web Apps using Angular 9
Debasis Saha
Build and deploy to any platform using Azure DevOps
Chervine Bhiwoo
Deep Dive in Azure Service Bus
Akshay Patel
Build a Native Mobile Application using React Native and JavaScript
Joseph Guadagno
Making sense of Web Job, Web Job SDK and Functions in Azure
Prakash Tripathi
CloudFront Distribution in AWS
Viral Jain
Tea Break
Introduction to PowerBI
Aakash Maurya
Build Advanced SPFx solutions with React and Graph API
Siddharth Vaghasia
Build Business Intelligence Analyst (BIA) Skills
Sundaram Subramanian
Deep dive of Power Platform – AI BUILDER
Prasham Sabadra
Panel 1
What's new in SharePoint development
Vipul Jain
Build a SSO (Single Sign On) based Native JavaScript application with Microsoft Identity within 10 minutes
Manoj Mittal
Panel 2
Applications and working of AI
Veena Sarda
Deploying serverless API's with .Net core 3.0 on AWS & Azure
Amey Vartak
Panel 3
Blockchain with .NET Core (Ark)
Anshu Kumari
Closing Note & Prize Distribution
Dev Track
Cloud Track
Architecture Track
Emerging Tech Track
Registration & Breakfast
Creating Full-Stack Web Apps Using Server-Side Blazor
Ankit Sharma
Real time face recognition with MS Cognitive Services
Niloshima Srivastava
Building Scalable APIs with GraphQL
Jeetendra Gund
Future of development with AI and Blockchain
Navdeep Garg
Debugging Tips and Tricks with Visual Studio 2019
Joseph Guadagno
Azure Containers
Abhishek Kant
Enterprise Architecture
Naveen Sharma
Bot Framework - learn it fast and look like a boss!
Allen O’Neill
Keynote
.Net Core & C# 8 Performance
David McCarter
Working with Azure kubernetes services
Ritesh Modi
Becoming an Architect
Vidyavrat Agarwal
Why Techies Need to Learn Product Management
Saurabh Jain
Lunch
Build a rules engine in .Net Core
Sanjay Vyas
Building CI and CD Pipeline using Azure DevOps
Sandeep Soni
Entity Framework Core - Tips and Tricks, Performance Optimization, and Tuning
Bassam Alugili
Hacking your way into Data Science
Sanket Verma
Speed up your .Net Core Website
Sourabh Somani
Azure
Magnus Mårtensson
Demystifying Open Distro for Elasticsearch
Suman Debnath
Future of Data
Shivam Ahuja
Tea Break
gRPC with C# and .Net Core
Mangesh Gaherwar
Panel 1
Essentials of Cloud security
Parveen Malik
Power platform and Dynamics 365
Deepesh Somani
Microservices - the gRPC Way
Viswanatha Swamy
Panel 2
Reserved
Reserved
Closing Note & Prize Distribution
Governing Azure Resources With Azure Policy
Cloud environments grow quickly. A development team can create a virtual machine in minutes, connect a storage account to an application, and deploy workloads across several regions before a central IT team has reviewed the design. That speed supports innovation, but it can also produce inconsistent configurations, unexpected costs, security gaps, and compliance problems.
Azure Policy provides a structured way to govern cloud resources without blocking every deployment manually. It evaluates resources against business and technical rules, reports noncompliance, blocks risky configurations when appropriate, and can automatically correct selected settings. Used well, it becomes a practical control layer for Azure subscriptions, resource groups, and individual services.
For developers and technology professionals familiar with Microsoft platforms, policy management is especially useful because it connects architecture standards with everyday delivery workflows. The same governance model can support application teams, DevOps engineers, security specialists, and financial stakeholders.
Why Azure Policy Matters
Azure Policy is a service for creating, assigning, and managing rules across an Azure environment. A policy definition describes a condition and an expected outcome. For example, a rule might require resources to use approved regions, enforce a specific tag, restrict public network access, or allow only selected virtual machine sizes.
The service is different from Azure role-based access control. RBAC answers the question, “Who can perform this action?” Azure Policy answers, “Is this resource configuration permitted or compliant?” A user may have permission to create a resource while policy still prevents the resource from violating organizational standards.
Policy also differs from Azure Blueprints, Azure Resource Manager templates, and Azure Automation. Templates help deploy known configurations, while policy continuously evaluates the resulting resources. Automation can perform operational actions, but Azure Policy supplies the governance decision and compliance record. Together, these tools create a stronger cloud management framework.
Governance should cover more than infrastructure security. A mature policy set can address data residency, naming conventions, encryption, backup requirements, diagnostic logging, approved SKUs, network exposure, and cost controls. Teams working with data-intensive services can also pair governance with stream processing guidance, ensuring that analytics workloads follow the same standards as other cloud resources.
Build a Policy Governance Model
Start by identifying the outcomes the organization needs. Security teams may prioritize encryption and private connectivity. Finance teams may need cost-center tags and region restrictions. Platform engineers may focus on diagnostic settings, managed identities, and resource consistency. Translating these goals into measurable controls prevents policy from becoming a disconnected collection of technical rules.
A policy definition generally contains a condition, an effect, and optional parameters. Parameters make a rule reusable. Instead of writing separate policies for every approved location, an administrator can create one policy with a list of permitted regions. The same approach works for allowed resource types, required tag names, and approved virtual machine families.
Policy initiatives group related definitions into a logical package. An initiative for secure storage might include rules for encryption, HTTPS-only traffic, private endpoints, logging, and minimum TLS versions. Assigning the initiative as a unit simplifies reporting and gives stakeholders a clearer view of the organization’s governance posture.
Use a hierarchy that matches how the business operates. Management groups can hold broad enterprise requirements, subscriptions can contain environment-specific controls, and resource groups can support application or team-level standards. Scope determines where a policy applies, while exclusions allow carefully documented exceptions for legacy systems, temporary experiments, or specialized workloads.
Choose the Right Policy Effects
The policy effect determines what Azure does when a resource matches the rule. Selecting an effect requires an understanding of deployment workflows, existing resources, and the risk associated with noncompliance. A production security requirement may justify a denial, while a naming convention may begin as an audit-only control.
| Policy Effect | Primary Behavior | Suitable Use |
|---|---|---|
| Audit | Records noncompliant resources without stopping deployment | Establishing visibility and measuring current state |
| Deny | Blocks creation or update when a rule is violated | Preventing high-risk configurations |
| Modify | Adds or changes selected properties during deployment or update | Applying tags or standard settings |
| DeployIfNotExists | Deploys a related configuration when it is missing | Enabling diagnostics, agents, or monitoring |
| Append | Adds a property to a request when it is absent | Supplying safe defaults for supported resources |
| Disabled | Suspends evaluation for an assignment | Temporary, controlled exceptions |
Audit is usually the safest starting point for a new governance program. It reveals how many existing resources would fail a proposed rule and exposes application dependencies that may not be visible from architecture diagrams. After teams understand the impact, selected policies can move to modify, deploy-if-not-exists, or deny.
The corrective effects require careful testing. A modify policy may add a tag, but it cannot solve every configuration problem. DeployIfNotExists often depends on a managed identity and a remediation task with sufficient permissions. Deny is powerful, yet an overly broad condition can interrupt automated deployments and create pressure to bypass governance entirely.
Use policy exemptions instead of silently excluding entire subscriptions or weakening a rule. An exemption should include an owner, reason, expiration date, and compensating control. Time-limited exceptions preserve accountability and make it possible to revisit technical debt rather than allowing it to become permanent.
Assign Policies At The Right Scope
Policy assignments connect definitions or initiatives to a management group, subscription, resource group, or resource. A rule assigned at a higher level applies broadly unless a narrower scope or exclusion changes its reach. This makes scope design one of the most important parts of Azure governance.
Enterprise-wide controls usually belong at a management group or subscription level. Examples include approved locations, mandatory cost tags, and restrictions on public IP addresses. Application-specific rules may be more appropriate at a resource group, especially when a workload has unusual data, networking, or performance requirements.
Assignment parameters help maintain consistency while supporting legitimate variation. A production subscription might permit only two regions, whereas a development subscription may allow additional locations. The policy definition remains the same, but the assignment provides the values that fit each environment.
Organize assignments so that ownership is obvious. Use meaningful names, descriptions, and metadata to identify the control owner, business purpose, review date, and expected remediation path. Consistent assignment conventions make governance easier to maintain through the Azure portal, Azure CLI, PowerShell, or infrastructure-as-code pipelines.
Operate, Monitor, And Remediate
Policy governance is an operating process rather than a one-time configuration. The Compliance view in Azure Policy shows which resources match or violate assigned definitions, helping teams identify trends by subscription, resource group, resource type, or policy initiative. A compliance percentage is useful, but the underlying resources and reasons require closer analysis.
Separate new violations from inherited technical debt. A storage account created yesterday with public access enabled may need immediate action, while an old application with a hard-coded dependency may require a migration plan. Treating every violation identically can create unnecessary disruption and encourage teams to ignore compliance reports.
Remediation tasks help correct existing resources for policies using modify or DeployIfNotExists effects. These tasks require appropriate permissions and should be tested in a controlled scope before being applied broadly. Review the resulting resource changes, especially when policies affect networking, identity, logging, or production data.
Integrate policy results into operational reporting. Azure Monitor, Microsoft Defender for Cloud, and service management workflows can provide additional visibility into high-risk violations. Development teams can review policy impact during pull requests or deployment validation, while platform teams can track recurring failures and improve reusable templates.
Use policy as code when governance rules need the same auditability as application code. Store definitions and initiative files in source control, review changes through pull requests, and deploy assignments through CI/CD pipelines. This approach supports repeatability across subscriptions and reduces the risk of undocumented portal changes.
Apply Governance Across Delivery Workflows
Good Azure governance starts before a resource reaches production. Infrastructure-as-code templates should include required tags, approved service configurations, and diagnostic settings wherever possible. Azure Policy then acts as a persistent control that evaluates deployments made through templates, the portal, scripts, or external tools.
A staged rollout reduces friction. Begin with audit policies, share findings with development teams, and fix templates that repeatedly produce violations. Next, introduce automatic modification for low-risk settings. Reserve deny effects for controls with clear ownership, reliable testing, and strong security or compliance justification.
- Define a small set of high-value controls before expanding the policy catalog.
- Use initiatives to group related security, cost, identity, and operational requirements.
- Test policy assignments in a development subscription or dedicated resource group.
- Record exemptions with owners, reasons, compensating controls, and expiration dates.
- Review compliance trends regularly and retire rules that no longer reflect the architecture.
Communication matters as much as configuration. Developers are more likely to adopt governance when policy messages explain the reason for a failure and show the approved alternative. A denial that says “deployment blocked” is less useful than a message identifying the required tag, permitted region, or supported SKU.
Conference sessions and technical communities can help teams compare governance patterns across Azure workloads, especially when policies affect cloud-native applications, data platforms, AI services, and DevOps pipelines. The most effective model is collaborative: security defines the risk, platform engineering builds the control, and application teams validate that the rule works in real delivery scenarios.
Build a small policy baseline, assign it to a controlled scope, and measure its effect on deployments and compliance. Then expand deliberately as the organization learns. Put Azure Policy into your infrastructure-as-code process, review exceptions on a schedule, and make governance a dependable part of every Azure release.
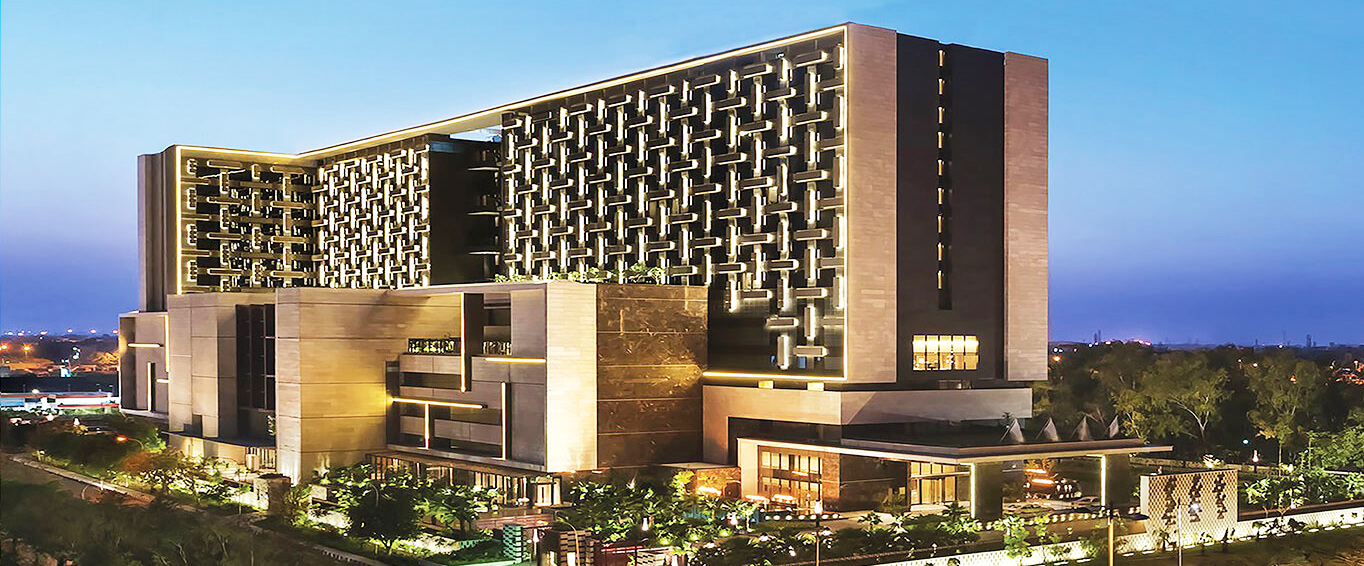
1, CBD, Maharaj Surajmal Road, Near Yamuna Sports Complex, Delhi, 110032
GENERAL QUERIES
Manish Tewatia
manish@csharpcon.com
+91-9718-431-042
TICKET QUERIES
Atul Gupta
conference@csharpcon.com
+91-9910-125-804